❌

Reading view

Longitudinal airflow suppresses train power-arc drift at low pressure

Longitudinal airflow can sharply suppress the drifting and ablation of the electrical arc formed between a train’s pantograph and overhead contact wire, according to a modeling and experimental study of pantograph–catenary systems under low-pressure conditions. The researchers built a magnetohydrodynamic model that coupled electric, magnetic, thermal, fluid and arc-motion dynamics, then tested the method in a vacuum chamber with copper and carbon electrodes. In experiments conducted at atmospheric pressure, increasing the airflow to 45 metres per second reduced the measured arc drift height from 27.6 millimetres to zero and shortened the arc-root distance from 51.3 to 3.9 millimetres. The same airflow setting also produced progressively less carbon-electrode damage, supporting the proposal as a possible current-collection control method for railways operating at high altitude.

The need for such control arises because the pantograph–catenary system carries the electrical energy used by electric trains, while the stability of its contact strongly affects operating safety and efficiency. Lower atmospheric pressure presents a particularly difficult environment. The study notes that reduced air density and breakdown-field strength can lower the ignition threshold for pantograph–catenary arcs, increase their frequency and duration, and enlarge the region affected by arcing. Repeated arcing can cause irreversible high-temperature ablation and electrical wear on contact wires and pantograph strips. It can also generate broad-band electromagnetic interference that may affect onboard signalling and traction-control systems, with potential consequences including insulator flashover and disruption of the traction network. These background risks motivate efforts to understand and restrain the spatial movement of arcs in plateau environments.

Existing arc models include the Cassie and Mayr black-box approaches, which support analysis of interactions between arcs and traction-network circuits but do not represent an arc’s changing spatial shape. Magnetohydrodynamic models offer a more physical alternative by coupling electromagnetic, flow and thermal fields. Previous work represented crosswind effects on pantograph–catenary arcs and examined how decreasing pressure affects arc-root jumping, in which the root forms at a new location after the elongated column reaches a critical length. Other studies have shown that magnetic fields can stabilize welding and switching arcs. Airflow regulation, however, has been investigated more extensively in welding than in pantograph–catenary systems, whose dissimilar electrodes, high operating speed, open environment, changing electrode gap and constrained vehicle installation space make their arc dynamics more complicated.

The new model represents an arc initially 6 millimetres long and 2 millimetres in diameter between a copper anode and a carbon cathode. It includes the surrounding air, both electrodes and a central longitudinal-airflow channel beneath the copper electrode, including a 1.5-millimetre control-airflow inlet. A separate inlet represents train-induced airflow and was set to 40 metres per second. Calculations covered pressures of 101, 80 and 60 kilopascals, longitudinal airflow from zero to 80 metres per second and a total simulation time of 25 milliseconds. Air properties were adjusted with pressure, while the electrodes were assigned distinct densities, resistivities, thermal conductivities and heat capacities. The governing equations represented electrical potential and current, magnetic-vector potential, mass and momentum conservation, energy conservation, viscous dissipation, Joule heating and net volumetric radiation.

The calculations use several explicit simplifications. Arc ignition is omitted, and the plasma is treated as being in local thermodynamic equilibrium. Flow in the air and arc domains is assumed laminar and incompressible, while metal vapour generated by electrode evaporation and phase change is excluded. These assumptions make it possible to examine large-scale arc motion and temperature distribution but prevent the simulation from directly calculating electrode mass loss, crack width or crater area. Copper was assigned the anode and carbon the cathode; a Gaussian distribution represented current entering through the copper electrode, and the bottom of the carbon electrode was grounded. The air boundary was treated as magnetically insulated, and the initial temperatures were set to 300 kelvin for the air and electrodes and 5,000 kelvin for the arc domain. The experimental apparatus was separate from the numerical model and provided direct physical measurements of damage.

Without longitudinal airflow, the simulated arc passed through two stages. During the first 10 milliseconds, its column elongated continuously, bent under airflow influence, and developed greater drift height and arc-root distance. From 10 to 25 milliseconds, the column and root distance fluctuated through repeated shortening and elongation. The authors associate this behaviour with the electrical and mechanical limits of the arc: once a column reaches a critical length, the voltage and energy available between the electrodes may no longer sustain continuous burning, and a shorter path of lower resistance may form on the electrode surface. The resulting root “jump” shortened the column before airflow stretched it again. Arc development became faster and both drift height and root distance increased as pressure fell. Temperature briefly exceeded 10,000 kelvin and reached a maximum within roughly two to three milliseconds before fluctuating, while arc voltage rose as the column lengthened and resistance increased.

Longitudinal airflow changed these trajectories in the simulations. As speed increased, drift height, root distance and temperature all declined, with the greatest reductions occurring at lower airflow speeds before the curves began to level off. At 101 kilopascals, the calculated drift height fell from 37.5 millimetres without control airflow to zero at 45 metres per second, while root distance decreased from 57.3 to 3.7 millimetres and temperature dropped from 12,900 to 8,650 kelvin. The airflow needed to eliminate drift was 45, 40 and 35 metres per second at pressures of 101, 80 and 60 kilopascals, respectively; speeds required to bring root distance below 5 millimetres were 45, 40 and 30 metres per second. The authors attribute the stronger response at lower pressure to reduced plasma density, which weakens the arc’s inherent rigidity, Lorentz force and thermal buoyancy, allowing airflow load to become a more dominant influence on its motion.

The temperature response also revealed a practical plateau. The researchers defined the optimal airflow speed as the point after which increasing speed by 5 metres per second changes arc temperature by less than 3 per cent. At atmospheric pressure this occurred at 40 metres per second, compared with 30 metres per second at 60 kilopascals. The reported temperature reduction was 33.8 per cent at 101 kilopascals and 38.1 per cent at 60 kilopascals. Airflow strengthened convective heat removal, which lowered plasma temperature and, in turn, increased deionization and reduced Joule heating. Once thermal exchange approached saturation and the minimum temperature required for self-sustaining arc combustion was approached, further increases in speed produced little additional cooling. The model therefore indicates that the airflow speeds required for control decline as ambient pressure falls.

Laboratory testing used a vacuum chamber capable of controlling pressure with an accuracy of plus or minus 100 pascals, a constant-current supply rated from zero to 150 amperes, an arc igniter, a fan with continuously adjustable airflow from zero to 60 metres per second, a high-speed camera and an oscilloscope. Airflow at the electrode outlet was measured with an anemometer accurate to plus or minus 0.5 metres per second. The camera operated at 6,400 frames per second with an exposure of five microseconds, while each two-second arc test was repeated five times and the mean was reported. Tests at 101 kilopascals used airflow speeds of zero, 20, 30 and 45 metres per second. Without control airflow, high-speed images showed increasing arc drift. At 45 metres per second, drift was virtually absent during the final development phase and root distance was substantially shortened, with observed morphologies broadly consistent with the numerical results.

The experiments also found reductions in carbon-electrode ablation that increased with airflow speed. Microscopy showed shorter ablation areas, smaller craters and narrower crack propagation as the controlled airflow rose. The maximum crack width was 66.7 micrometres without airflow and decreased at higher speeds, while analytical weighing showed progressively less mass loss from the carbon electrode. The proposed mechanism is that stronger airflow promotes arc-root slippage, shortening the time the root remains at one point, while convective cooling lowers temperature and local energy density. These are experimental observations rather than direct outputs of the simulation: because the model omits electrode evaporation and metal-vapour transport, it cannot quantitatively predict ablation rates or near-electrode energy balances. The study therefore demonstrates reduced damage under its controlled laboratory conditions, not a complete first-principles calculation of all processes responsible for electrode wear or a proven field performance level in operating plateau railways.

Subject of Research: Experimental and numerical evaluation of airflow control of pantograph–catenary arcs at low pressure.

Article Title: Research on regulation method for suppression of pantograph-catenary arc by airflow in low-pressure environment

Article References: Xu, Z., Wang, S., Dong, K., & Gao, G. (2026). Research on regulation method for suppression of pantograph-catenary arc by airflow in low-pressure environment. iScience, 29(11), Article 117951. https://doi.org/10.1016/j.isci.2026.117951

Image Credits: AI Generated

DOI: 10.1016/j.isci.2026.117951

Keywords: pantograph–catenary systems, railway electrification, electric arcs, low-pressure environments, longitudinal airflow, magnetohydrodynamic modelling, electrode ablation, high-speed rail, plateau railways, arc suppression, Research, regulation
  •  

AMD brings official Ryzen overclocking to Linux with AOD driver support

While Windows overclockers have spent years lazily sliding UI controls to adjust frequency curves and tweak voltages inside Ryzen Master, Linux users have largely had to treat their CPU tuning like an archaeological dig into the opaque veil of UEFI/BIOS firmware. Well, rejoice, Linux users, as AMD has officially published a fresh set of patches for the Linux kernel introducing AOD (AMD Overclocking Driver) support for Ryzen processors, Phoronix reports.

Instead of forcing developers to reverse-engineer closed-source firmware hooks or rely on messy, machine-specific ACPI workarounds, this new kernel driver is a direct pipeline to AMD's platform adjustments. By exposing core tuning capabilities straight through the standard sysfs interface, AMD is laying down an official, upstreamed foundation for software-level CPU management.

Right out of the gate, the driver handles platform-level SMT toggling, memory clock visibility, and power tunables. That's right: you can now toggle Simultaneous Multithreading (SMT) dynamically through this driver interface. That works through the CPU hotplugging mechanism and acts as a clean alternative to passing the old 'nosmt' boot parameter to the kernel. The new driver also allows real-time monitoring of memory clocks, and initial power controls are being wired up, too.

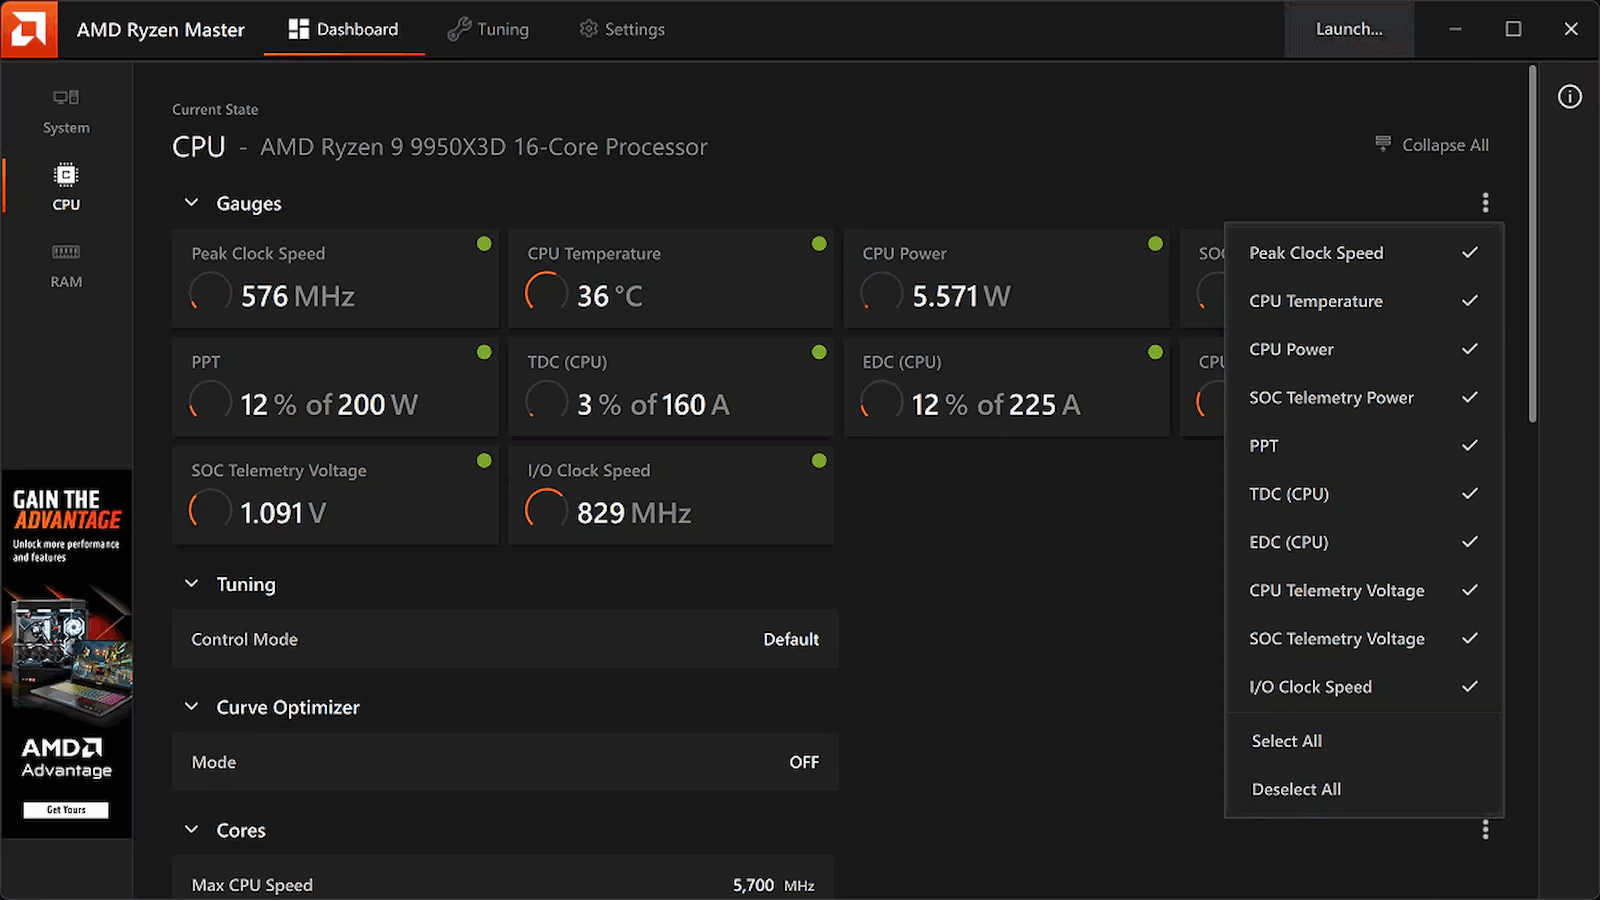
A screenshot of AMD's Ryzen Master CPU tuning tool.

This tool isn't available on Linux, and may never be, but at least its functions will be soon. (Image credit: AMD)

Now, if you're expecting a polished, one-click official AMD application equivalent to Ryzen Master for Linux, just pump the brakes. AMD is following its open-source amdgpu graphics driver playbook here, building the kernel plumbing and then leaving the user-space presentation layer entirely up to the community. That means you're going to have to wait for utilities like CoreCtrl to build out interfaces for this new driver, but it shouldn't be long now before that work gets underway in earnest.

This approach is arguably a better fit for the Linux philosophy anyway. Because the controls are being exposed via clean kernel sysfs nodes, it won't be long before independent developers integrate these knobs into powerhouse open-source monitoring and tuning suites, or even write dedicated desktop environment extensions specifically for the purpose of tweaking Ryzen processors.

The new patches are currently winding their way through review on the mailing lists, meaning mainstream kernel integration is on the horizon. For a DIY enthusiast who loves squeezing every last MHz out of silicon while maintaining a fully open-source software stack, this is easily the most exciting hardware-enablement milestone I've seen in a long time.

  •  

UK to Headphone Dodgers on Trains: Shush

Prime Minister Andy Burnham announced a campaign against listening to music or videos without headphones on public transportation. We asked London commuters to weigh in.
  •  

Tens of thousands of Nvidia GPUs sit idle in Meta's Prometheus supercluster, just waiting for a failure

More than 11 percent of the GPUs at Meta’s Prometheus supercluster in New Albany, Ohio, are either dead or sitting idle waiting to step in when the next drops out, Zuckercorp revealed this week. The massive pool of redundant GPUs is just one of several measures the hyperscaler has taken to keep its AI training runs on track. Prometheus is among Meta's largest compute deployments to date. Powered by Nvidia's Grace Blackwell and (soon) Vera Rubin rack systems, Meta says the supercluster will eventually scale to a gigawatt of capacity spanning about a million accelerators. But as anyone who has worked on a large scale compute cluster understands, whether for LLM training or traditional HPC workloads, more chips inevitably means more problems. In an eight-GPU node, the chance of having a GPU fail is relatively low. In a 100,000-GPU cluster, failures are unavoidable. Meta is building something that's 10x larger and requires distributed training runs across multiple datacenters. Keeping the entire thing humming long enough to reach the next checkpoint becomes a major headache. In a blog post published this week, Meta offered a unique look at the work it's done to keep failures from derailing the development of models like Muse Spark or its most recent release Muse Wonder. Idle GPUs are the cost of continuity When Meta began the first phase of its Prometheus deployment in New Albany, the company says, it was experiencing roughly 1,000 interruptions per day for every 8,000 GPUs. Interruptions don't mean GPU failure. They simply mean something crashed, failed, or timed out, forcing the training run to stop and roll back to the last known good checkpoint. Meta claims in the year since it's been able to cut down the number of interruptions by 99 percent, to about 11 per day per 8,000 GPUs. One of the ways it's done this is by keeping some of Prometheus' GPUs in reserve. The cluster is currently powered by a combination of GB200 and GB300 systems, each with 72 GPUs per NVLink domain. However, only 64 of them are ever in use at any given moment. The other eight are essentially hot spares. Meta did this because a single failed GPU would take out an entire rack and interrupt the training run. Now, when a GPU fails, one of the spares can slot in and take its place. While this saves time — Meta doesn't have to drop the entire rack from the cluster or wait for someone to swap the faulty component to start training again — a failed GPU would still result in an interruption, albeit a shorter one. Parallel resiliency To mitigate this, Meta took advantage of the fact that large scale training jobs usually use data parallelism, where multiple copies of the model are resident within the cluster. "When a fault can be isolated to a data-parallel model replica, we reduce the impact of a hardware failure by allowing a single faulty replica to be taken offline, while the remaining cluster repeats that step and continues productive training," Meta explained. "The compromised slice simply restarts on available spare hosts and resynchronizes, converting a potential total system halt into a minor, temporary reduction in aggregate throughput." In other words, Meta's training runs only get interrupted if the fault exceeds the data parallel domain. When this happens, the company has implemented a comprehensive checkpointing scheme, which you can think of a bit like auto-save or a revision history. That way if something does fail, Meta doesn't have to start over from scratch. "Our distributed checkpointing architecture asynchronously saves the model state — including gradients and optimizer data — to multi-tier storage," the company wrote. NVLink growing pains Meta says one of the most difficult challenges was making the NVLink fabrics used to connect 72 GPUs behave like one great big accelerator. Earlier H100 and H200-based systems featured just eight GPUs per NVLink domain, which meant the links were far shorter and less numerous. But this functionality was expanded nine-fold with Nvidia's Blackwell generation. "With over 600,000 NVLink connections, even marginal signal degradation triggers frequent NVLink recovery cycles," the company wrote. To overcome this, Meta had to implement a continuous telemetry system and conduct L11 diagnostic burns to isolate weak links before the systems were put into production. Power was another challenge. Ramping up and down tens of thousands of GPUs for a training run can introduce massive spikes in power consumption called transients, which can overwhelm power supply equipment. According to Meta, by focusing on the stability and reliability of its cluster, it was able to achieve more than 85 percent "goodput" — a measure of useful throughput — for pretraining and more than 90 percent for reinforcement learning on its latest model Muse Wonder. The company's ambitions don't stop here. As it works its way toward a million GPUs, Meta hopes to get its interruption rate down to just two per day for every 8,000 GPUs, or about 100,000 GPU-hours mean time between interrupts. ®

  •  

The Googlebook work test: Can an Android laptop get the job done?

In a weird way, I’ve been thinking about the idea of a Googlebook for well over a decade now — despite the fact that such a product has only officially existed for a matter of months.

I’m relatively unusual in the world of tech journalism, y’see, in that I’ve been both writing about Android and ChromeOS since the platforms’ earliest days and actively using devices from both ends of those ecosystems in my own day-to-day life that entire time. Most tech writers tend to be iPhone owners and Chromebook skeptics who see this part of the digital world from an outside view — once a year or so, when significant new devices come along for assessment — without having the perspective of someone who’s truly immersed in it day in and day out.

That distinction is always painfully apparent when you read a review that waxes on endlessly with out-of-touch iPhone comparisons and comments about the limiting nature of Google’s ChromeOS concept — positions that simply aren’t accurate for those of us who live in these ecosystems and embrace the philosophies they offer.

This won’t be one of those reviews, and I perhaps more than anyone have been champing at the bit to get my hands on one of Google’s new Android-ChromeOS-combining Googlebooks since the vaguest concept of these devices first appeared on the horizon earlier this year.

So keep that in mind when I tell you, coming from the perspective of someone who very much wanted to love this: Using a Googlebook is an extraordinarily strange experience — especially when you’re treating it like a regular laptop, as it’s being positioned by Google, and relying on it to get real work done.

But amidst all the oddness, there are some true high points along with plenty of intriguing, if unfinished-feeling, potential.

Here’s what it’s been like trying to actually work on a Googlebook — specifically, the Lenovo Googlebook, which sells for $1,149 (and was provided to me as a short-term loaner from Lenovo for the purposes of this article).

The Googlebook groundwork

First things first, let’s back up a minute and set the stage for what we’re even talking about here.

The Googlebook is a new type of laptop created by Google and built by a variety of third-party device-making partners — Acer, Asus, Dell, HP, and Lenovo, to start.

It’s meant to represent an evolution of sorts from the Chromebook, the initially simple laptop Google launched in 2012 and slowly morphed from a barebones web portal into an “everything OS” — a system that runs web apps, Android apps, Linux apps, and even sometimes Windows apps, for businesses that have specific needs that can’t be addressed in any other way.

But while ChromeOS and Android grew closer and more connected over time, Googlebook OS — the awkwardly clunky name of the operating system at the heart of every Googlebook — sets all of that aside to aim for a fresh start. The software here sports Android at its core alongside a variety of optimizations designed to bring in bits of ChromeOS-like elements and make everything seem more suited to a laptop setting.

With that in mind, starting to use a Googlebook is both immediately familiar and vexingly confusing. The interface feels a lot like Android, which is nice, but it also doesn’t quite feel in line with how you expect to work on a desktop computer. It’s a jarring sort of mashup, and it’s tough to wrap your head around to get comfortable working.

That’s true for relatively small touches like having the clock in the upper-left corner of the screen instead of in the lower-right corner, where’d you expect it on most non-Apple-made computers. It’s a little thing, but it keeps throwing me whenever I try to glance at the time during the day. That approach is similar to Android, yes, but it just doesn’t feel right in this environment or with what pretty much all of us who’d be considering this kind of device have been trained for ages to expect with a desktop computer experience.

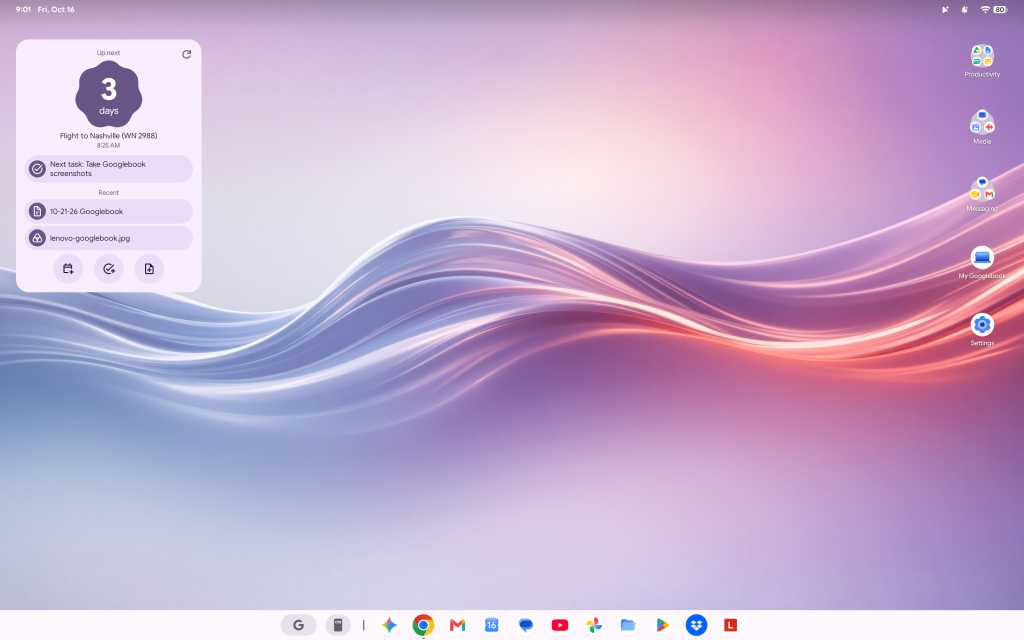
screenshot of mostly empty googlebook desktop

The Googlebook’s desktop is similar to Android — but that doesn’t immediately feel natural in a desktop computing environment.

JR Raphael / Foundry

It’s true, too, for keyboard shortcuts, which don’t work the same as they did on ChromeOS — even just basic, common things like opening items on the taskbar. (Googlebook OS does have an impressive array of customizable keyboard shortcuts, if you find ’em, but there’s a ton of new combinations and muscle memory to be learned.)

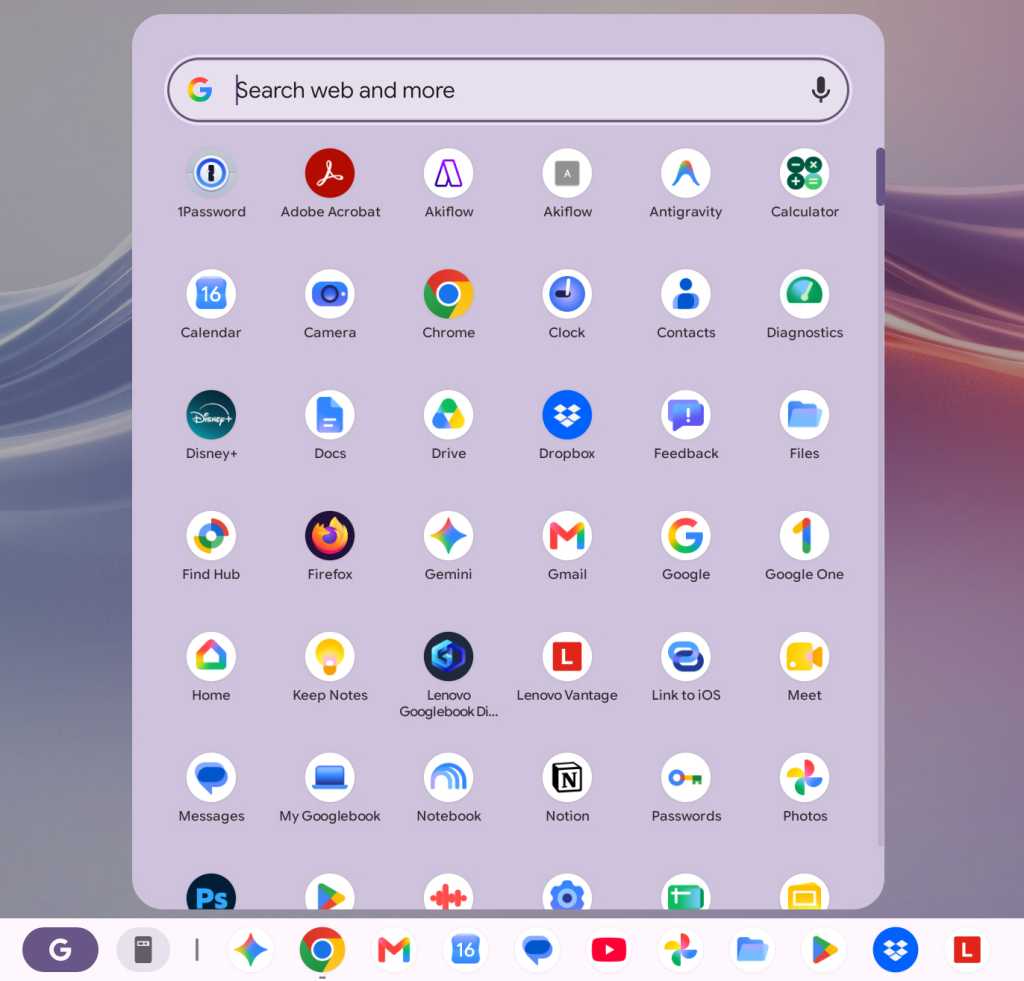
The confusion is probably most prominent, though, on the app front, where Google is really leaning hard into the Play Store and the idea of Android apps being the primary way to get stuff done, despite the fact that Android apps often aren’t ideal — or even available, in some instances — in a productivity-oriented, desktop computing scenario.

screenshot of googlebook apps list

The Googlebook app experience revolves primarily around the Play Store — which can be a pro or a con, depending on the moment.

JR Raphael / Foundry

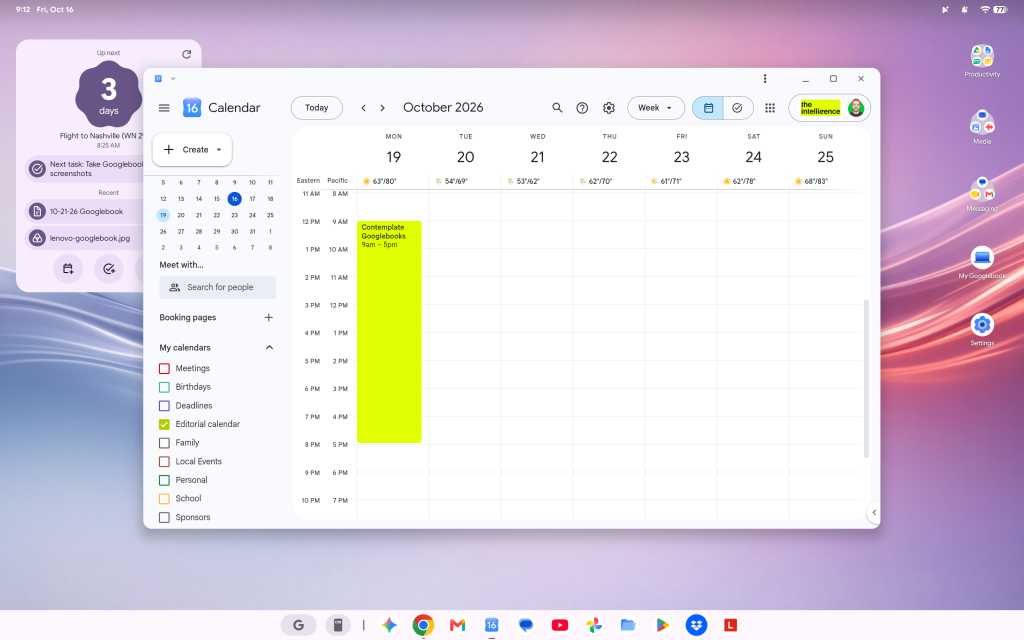
At least one of Google’s own apps addresses this elegantly. Installing Google Calendar from the Play Store basically just gives you an app-like shell around the Calendar website, and you can use the Android app’s widget alongside that, if you want. (The downside is that you can’t use the equivalent Android app in full even if you want to, as there’s no straightforward path to install it — and, strangely, the same web-widget combo is not available with other Google apps, like Gmail or Drive, which give you only the web version and no option to use any associated Android widgets.)

screenshot of google calendar app on a googlebook

The Google Calendar app on a Googlebook is basically just the Calendar website, though you can still use the Android app’s widget alongside that.

JR Raphael / Foundry

And since the version of Chrome on a Googlebook looks and feels like the full desktop version of the browser — like what you’d expect on a Chromebook or any other desktop computer — relying on this unusual mix of web and Android interfaces for productivity is mostly OK. Mostly.

Working in Docs, with as few as five or six tabs open, I continue encountering an occasional issue where the tab just blanks out for a second or two and then comes back — which, suffice it to say, isn’t exactly optimal for working.

The email app I use, Superhuman, appears to be completely incompatible here. The web version (which is powered by a Chrome extension) errors out anytime I open it, and the Android app is clearly not meant for large-screen, keyboard-and-mouse use and presents an incredibly awkward experience as a result.

The productivity tool Notion, meanwhile, came up for me as one of the Googlebook’s suggested tools that’s optimized for desktop use, so I followed that direction and installed the Notion Android app — only to find that the app is much more awkward and limited on a laptop than the regular Notion web experience, where all the functions are available and the keyboard shortcuts work as expected. So I decided to try to install the Notion web app for easy ongoing access to that, and I encountered a mysterious error.

width="787" height="378" sizes="auto, (max-width: 787px) 100vw, 787px">

Trying to install certain common web apps results in a frustrating error.

JR Raphael / Foundry

D’oh.

Then there’s something like Slack, which you can install from the Play Store but with an accurate warning that it’s “better on the website.” So, OK: You go to the website, try to sign in and install the web app version of it from there, and…there’s that blasted “cannot be installed” error again. (Google says it rolled out an update last week that allows any web page to be installed as a web app, but as of this writing — even with that update present on my device — the same error-encountering pattern persists.)

Other apps appear to work fine but then behave in odd and unexpected ways. I tried to install the Android version of Vivaldi, for instance, and it installs and opens without issue — but then returns an error anytime I try to actually open a website within it. That definitely doesn’t happen on a Chromebook, nor do the other aforementioned issues.

There’s just a lot of weird stuff like that, where it feels like a typical Google not-quite-fully-baked product. To be fair, that may be at least in part because of third-party app developers not yet supporting what needs to be supported for full optimization in this new environment — but either way, that’s the experience you get on a Googlebook right now, and it’s an all-too-familiar chicken-and-egg challenge that there’s no telling how long might take to see resolved.

On a somewhat related note: While the ability to install Linux apps is technically present on a Googlebook, it isn’t at all a user-friendly experience. Linux app installation is available only in a limited manner within the confines of a command-line terminal, and any such programs consequently don’t integrate into the launcher or the main Googlebook interface. That means there’s no real way to use them as a part of the standard Googlebook experience — which is a shame, as having those more traditional desktop apps available on ChromeOS went a long way in filling in pertinent function gaps for a lot of people and businesses. (Google says better Linux app support is vaguely “on the roadmap.”)

The various layers Google created to make Windows apps available for businesses in ChromeOS aren’t present in this environment, either. The official line, as relayed to me by a Google spokesperson, is that “Googlebook takes a fundamentally different architectural path than previous platforms” and they “aren’t attempting to patch together legacy PC software layers or rely on Windows emulation to make a laptop functional”:

Instead, Googlebook OS is built directly on the Android tech stack with the desktop foundations of ChromeOS, pairing the world’s largest native app ecosystem with an uncompromised, full desktop Chrome browser.

This makes it easier than ever for developers to build a true desktop-class app experience.

That’s all noble enough in theory — but as a prospective Googlebook owner right now, what good does any of that do when most developers haven’t yet built those “true desktop-class app experiences” for this environment? Or when you’re a business user whose company has the very same sort of “legacy” software requirements that led Google to work so hard on Windows app support for Chromebooks and maintain that option in that arena?

Pros, cons, and more Googlebook confusion

Let’s break from the strange stuff for a minute to focus on some positives — because, again, there is something undeniably cool about experiencing Android in a laptop form and seeing all the ways a Googlebook works hand in hand with an Android phone to make life easier.

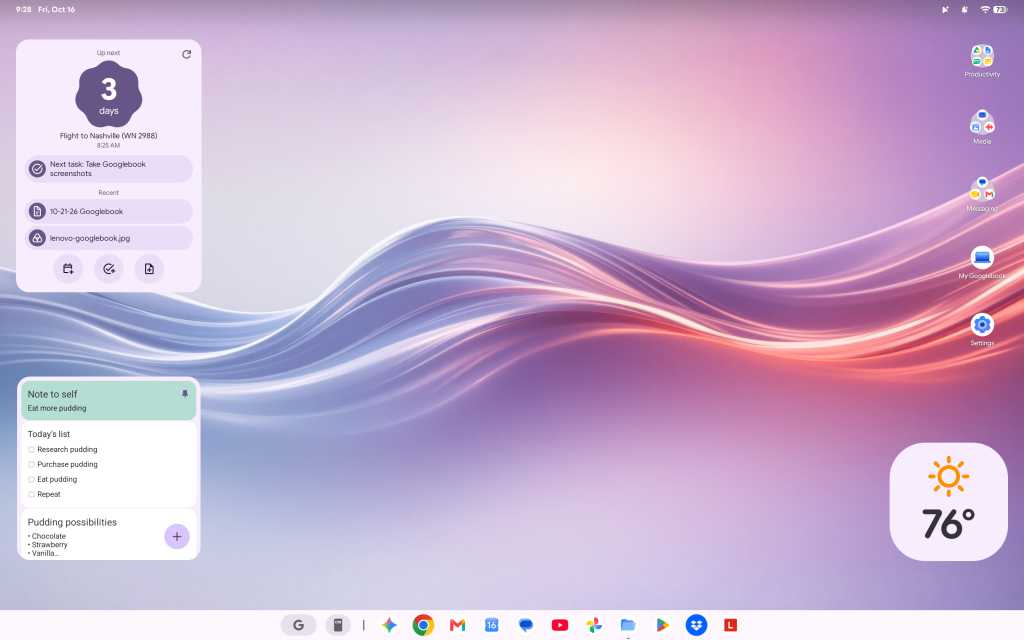
First and foremost, Googlebooks stray from the longstanding minimalist Chromebook standard to give you a fully customizable desktop — with the ability to create any arrangement of shortcuts and widgets, just like you can on an Android home screen. That is absolutely a welcome progression from the more limiting ChromeOS approach and something I’d long hoped to see in that domain, and having those familiar forms of interactive info right in front of you while working is an incredibly helpful addition.

screenshot of googlebook desktop with widgets

Having a fully customizable desktop, with regular Android widgets available, is a significant leap forward for the Googlebook.

JR Raphael / Foundry

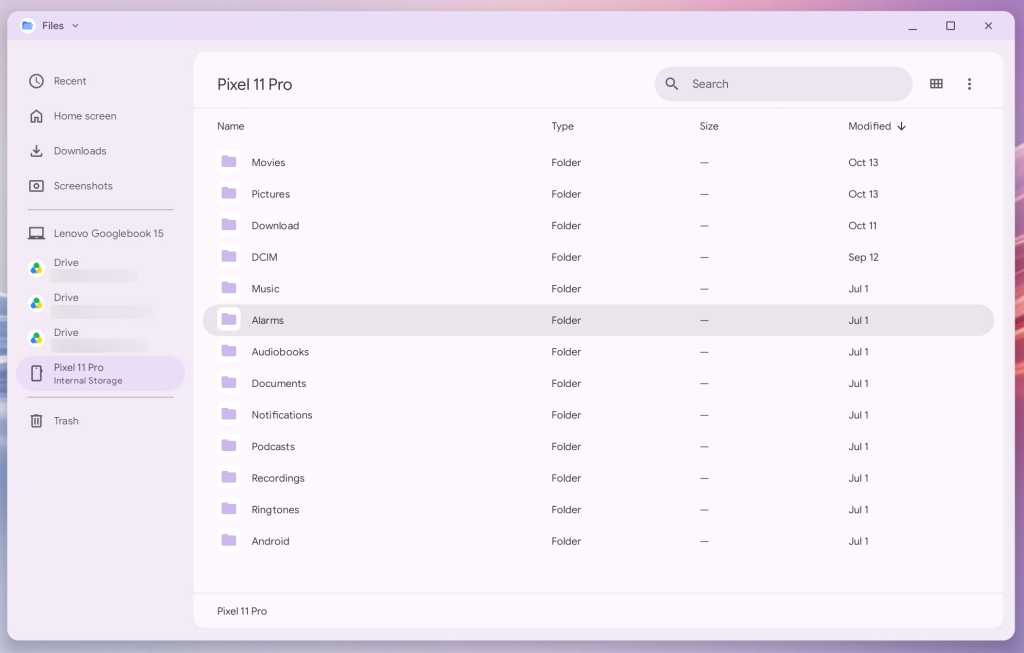
Being able to easily access the files on your phone without any extra hoop-jumping is also a nifty touch, for the moments when such a need arises. Once your Googlebook is paired with your Android phone, you simply open the Files app on the laptop, and you can see and interact with any files on your phone right then and there. (That said, the Files app is otherwise much more barebones and limited than its ChromeOS equivalent, unfortunately — so you can’t, for instance, drag and drop directly from the phone to any specific folder on your local or Google Drive storage.)

screenshot of files app showing files on a pixel 11 pro phone

The Googlebook makes accessing files on your Android phone delightfully easy.

JR Raphael / Foundry

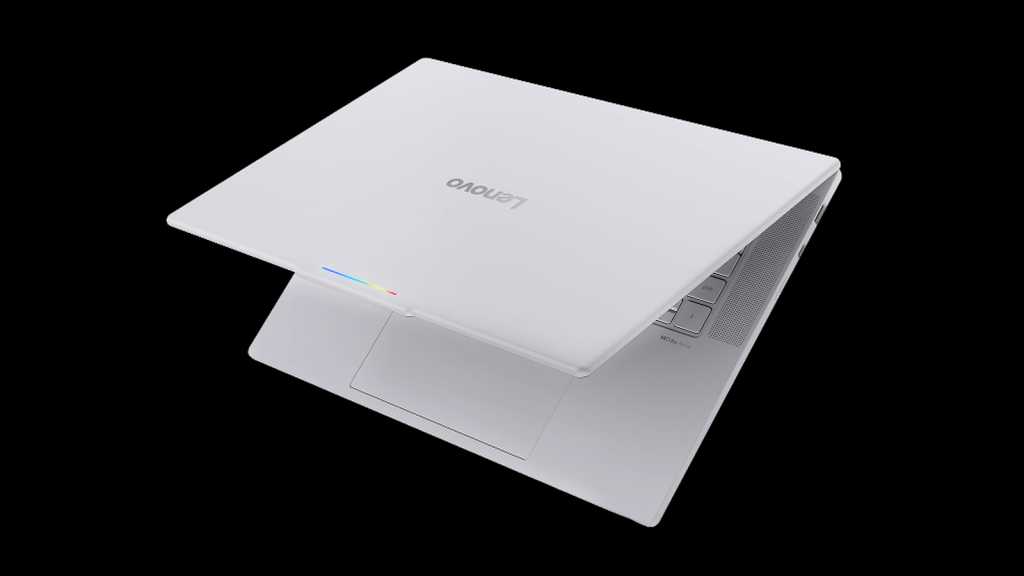
As far as hardware is concerned, Lenovo did a bang-up job with its inaugural Googlebook device. This is one seriously nice laptop — a pleasure to hold, with an almost silky-feeling smooth texture on the top and a thoughtfully ridged bottom for extra grippiness when you carry it. The system has a beautiful (and big!) 15.3″ display, an excellent keyboard and trackpad, and surprisingly great speakers. Those boxes are all checked off.

photo of lenovo googlebook with lid partially open

The Lenovo Googlebook is a sleek and premium laptop with all the right elements in place, as far as hardware is concerned.

Lenovo

But it’s the experience inside the hardware that means the most, here in particular — so, back to that:

Native app installation aside, one key selling point of the Googlebook is how it’s able to stream apps from a connected Android phone — letting you run an app from your phone on the computer, in other words, without having the app installed locally on the Googlebook itself.

It’s a slightly confusing concept to wrap your head around, especially since you can also install most of the same apps from your phone directly onto the Googlebook if you want (and, given that this is a native Android device, installing and running Android apps on it is absolutely smoother and snappier than what you typically experience on a Chromebook). Because of that — just like with the equivalent streaming option that had been available on ChromeOS in recent years — it seems like something that’s bound to be more befuddling than beneficial for most people, most of the time.

width="652" height="1024" sizes="auto, (max-width: 652px) 100vw, 652px">

Android app streaming presents some perplexing overlap by allowing you to remotely run many of the same apps you could also install directly on the Googlebook.

JR Raphael / Foundry

That being said, I have had a couple of situations come up where it seemed like the feature might be handy. First, I needed to get a two-factor authentication code out of Authy, which is available only as a mobile app. A perfect use-case, right?

Well, not exactly: The Googlebook wouldn’t let me stream the Authy app from my phone and instead gave me an error: “Can’t cast content. This content is restricted.” So then I thought maybe I’d just install Authy directly onto the Googlebook instead, but alas: The app “isn’t available on Google Play on this device.” Bah.

Another time, I tried to open Google Wallet from my phone to get some info off my insurance card, which I have stored in that service. That worked, at first — but then the app kept hanging on a loading screen anytime I tried to open anything.

The one scenario where the app streaming has been helpful is with notifications: Anytime you get a new notification on your connected Android phone, it shows up as a pop-up in the upper-right corner of the Googlebook display. The same actions that’d be present on the notification on your phone, such as marking something as read or replying in-line, are also present on the computer, and you can click on the notification to open the associated app in full on your laptop — just like you would on your phone, only everything happens within a window on the Googlebook.

That’s a clever little sleeper feature and arguably the best part of the app streaming capability, even if you don’t necessarily think about the fact that you’re using app streaming when it happens.

Another key selling point is the addition of AI-oriented features into the Googlebook operating system. This includes a Magic Pointer feature that lets you wiggle your cursor to summon Gemini and ask it about any specific area of text or visual on your screen — which is fine but not something I find myself actually using often. Its most useful-seeming promise is being able to act on information, like creating a calendar event based on a specific area of an email or text message on your screen, but its accuracy in getting the details right in such scenarios has been pretty hit and miss in my experience.

Then there’s the integrated Rambler system for conversational voice-to-text conversion (as seen on Google’s recent Pixel phones). It works well, but by design it isn’t a direct dictation tool; instead, it adjusts and rewrites your rambling speech (hence the name) to make it better, in its view. That makes a lot of sense when you’re spouting off a quick text message while walking or driving, but unless you don’t mind losing your own specific style, intentions, and voice with longer computer-crafted communications, it doesn’t seem like something you’d be using much in a business capacity — though it can certainly be handy to have available on occasion.

As is often the case with Google products and AI features in particular, some of the smaller, less headline-making touches on the Googlebook are much more interesting than the flashy marquee features.

All in all, it’s a perplexing picture.

The Googlebook productivity puzzle

More than anything, the question that keeps coming to my mind — again, as someone who fully embraces Android and frequently works on a Chromebook — is simply: Who is this meant to serve? And, in its current state, for whom will it be a meaningful upgrade and enticement over other existing options?

I keep thinking how this exact setup would make for an absolutely brilliant souped-up Android tablet interface, with the right kind of hardware around it. You’d have the familiar Android-like environment, optimized for a larger screen, and the ability to pair that with a more desktop-like experience in the core Google apps — including Chrome, for a less limiting active web experience when you connect a keyboard (or flip around a convertible device to have one present).

As the Googlebook stands now, though, I just don’t know that it’s a great replacement yet for a Chromebook — or any other laptop — particularly when it comes to getting actual work done. At best, it feels like a fairly linear progression with some awkward adjustments and asterisks. At worst, it’s gonna be a real challenge for some people to use in the way they need a laptop to work. And I’m just not sure what’s being added, from a practical perspective, that makes it all worthwhile.

What we can say is that Google has a history of launching products that are still rough around with the edges, and sometimes, those products evolve over time — sometimes quite quickly! — and end up becoming incredible. Heck, think how much ChromeOS changed from its earliest form to the way it is today.

At the same time, Google also has a pesky habit of pivoting, giving up, and failing to follow through on once-heavily-hyped products. A fair amount of the Googlebook’s early shortcomings come down to convincing third-party developers to buy into the platform and invest the resources in making their apps work well on it, too — which is the exact same chicken-and-egg challenge that’s kept promising Google concepts from blossoming before.

For now, the Googlebook is an awkward start with plenty of potential. Where it goes next is anyone’s guess — and something that, to some degree, may depend on how many people are willing to take the leap with it early and wait for it to evolve.

  •  

Fungi help pine trees survive heat stress

In hot weather, trees “sweat” to cool down by releasing water from their leaves or needles and then replacing it with water from the soil. But during long periods of high temperatures, trees may release more water than they can replace. To strengthen forests against heat stress and other environmental hazards, scientists have suggested adding fungi to the soil. 

Soil fungi living on tree roots are called ectomycorrhizal fungi. They help trees absorb water by expanding their root networks, and trees help the fungi by providing them with sugars for energy. This beneficial partnership is known as symbiosis. Scientists at Fujian Agriculture and Forestry University in China tested whether symbiosis with ectomycorrhizal fungi could help the pine trees Pinus massoniana survive warmer temperatures. 

For their experiment, the researchers grew pine seedlings with and without ectomycorrhizal fungi in a greenhouse under different temperature conditions. First, they grew fungi called Cenococcum geophilum for 45 days on a gel-like substance called agar. At the same time, they grew the pine seedlings for 30 days, then transferred them into pots with natural soil. 

After 15 days in the pots, the researchers spread the gel-like agar containing the fungi over small 1 x 1 centimeter (cm) areas of the pine root tips to introduce the fungi to the seedlings, a process called inoculation. They assumed that the fungal network would expand from the starting area to colonize new root tips as the seedlings grew. The team’s inoculations included 6 different C. geophilum strains and 1 fungi-free control. To simulate heat stress, the researchers replicated each of the 7 inoculations at 25°C (77°F) and 35°C (95°F). They repeated each inoculation condition in 3 pots with 3 seedlings, for a total of 126 seedlings. 

After 60 days, the researchers harvested the pine seedlings and used a microscope to count how many of their root tips had fungi. They divided the number of root tips with fungi by the total number of root tips to calculate a colonization rate. They considered seedlings with a colonization rate of 80% or higher to have successfully formed a symbiotic relationship with the fungi. Then, the researchers analyzed seedlings with an 80% colonization rate to investigate their symbiotic partnerships.

The team observed that pine seedlings grown under heat stress at 35°C were 24% to 59% smaller than those grown at 25°C, and their needles were yellow instead of a healthy green. However, the seedlings that formed a symbiotic relationship with the ectomycorrhizal fungi were greener and 80% heavier than the control seedlings. 

Investigating the trees further, the team measured 3 chemical compounds related to plant stress, including malondialdehyde (MDA), proline, and nitric oxide. Plants release MDA when damaged, so high MDA levels mean a plant is struggling. In contrast, plants release proline and nitric oxide to repair cells or hold water, so high amounts of these compounds mean a plant is healing.

To measure MDA and proline levels in the pine needles, the researchers mixed them with different acids that change color depending on the sample’s MDA or proline content. To measure nitric oxide, the researchers mixed the needles with a protein that converts the compound into a chemical that changes color. They found that inoculated seedlings at 35°C had about 30% to 40% less MDA, 15% to 30% more proline, and 150% more nitric oxide in their roots than the control seedlings. 

Finally, the researchers measured changes in gene activity in the inoculated pine seedlings. They identified active genes by analyzing RNA molecules from the pine seedling roots with a process called RNA sequencing or transcriptomics. They found that inoculating the seedlings with ectomycorrhizal fungi activated more genes related to root strength, water retention, cell defense, and general plant protection than were activated in the control seedlings. 

By combining chemical analyses with growth measurements, the team concluded that a symbiotic partnership with the ectomycorrhizal fungi helped the pine seedlings survive heat stress. They demonstrated that through prolonged heat, inoculated seedlings maintained greener needles and lower levels of stress chemicals. They suggested that ectomycorrhizal fungi could be an ecological tool to help trees stay hydrated in a warming world. They recommended that future researchers conduct field trials with inoculated trees to translate these findings into forest management strategies. 

The post Fungi help pine trees survive heat stress appeared first on Sciworthy.

  •  

October Patch Tuesday: 1,408 CVEs, 1 exploited flaw and a SharePoint surprise

Microsoft’s October 2026 Patch Tuesday is the year’s largest release, with 1,408 CVEs requiring customer action, 72 of them rated critical. September, the previous high, carried 963. One CVE is already exploited: CVE-2026-96951, a Windows Shell flaw that bypasses Mark of the Web. Two were publicly disclosed before release, in the .NET Framework and the MessagePack-CSharp library. Separately, on 25 September Microsoft reported attacks against CVE-2026-65660, a SharePoint Server flaw fixed in August. Readiness recommends a Patch Now scheduling for Windows, Office, Exchange and the developer tooling, and a standard release schedule for SQL Server. The Readiness team has published an infographic summarising deployment risk by product family.

Known issues

On 14 October, Microsoft added a known issue to this month’s Windows 11 updates, KB5127648 for versions 24H2, 25H2 and 26H2, and KB5127646 for 26H1. Non-admin users might be unable to open Remote Desktop connections to devices that have Administrator protection enabled, with error 0xC000000D. The issue started with September’s non-security preview update. The Windows 11 security baselines enable Administrator protection by default, so test remote access to managed hosts before broad deployment. Microsoft’s mitigation is to turn off Administrator protection temporarily through your policy management tool, and a fix will follow in a future update.

Two issues remain open:

  • Some USB Audio Class 1.0 devices might fail to start or produce no sound. The 14 September out-of-band update resolved part of this, and for the remaining symptoms Microsoft directs IT administrators to Microsoft Support for Business.
  • Windows Server Update Services still does not display synchronisation error details on Server 2025 and Server 2022. Microsoft removed the function to address CVE-2025-59287 and offers no workaround.

And three are now closed:

  • The incorrect “Microsoft Defender Antivirus is turned off” notifications, still open when we published in September, were fixed by Defender Antivirus update 4.18.26080.4, released on 17 September.
  • On Windows 11, the October update fixes Explorer failing to start after sign-in on multi-user systems such as Azure Virtual Desktop with FSLogix, which left users at a black screen.
  • On Windows 10, Windows 11 23H2 and Server 2016 and 2019, it fixes File History failing to back up or restore and showing a false “Reconnect your drive” message.

Major revisions and mitigations

Between the September and October releases, from 9 September to 12 October, Microsoft’s Security Update Guide notifications covered 111 entries for Microsoft’s own products, not counting Chromium republications for Edge. Of those 111, 90 are true revisions rather than new entries. September’s window had one.

  • On 17 September, 84 of September’s CVEs gained Office for Mac updates. Each revision note tells customers running affected Mac software to “install the update for their product to be protected”.
  • On 16 September, Microsoft corrected the scoring of three critical SQL Server remote code execution flaws from September, CVE-2026-67378, CVE-2026-67631 and CVE-2026-67643. The scores now record that “an attacker does not require any privileges”. Microsoft calls this an informational change.
  • On 25 September, Microsoft revised CVE-2026-65660, a SharePoint Server remote code execution flaw fixed in August, to state that it “had reliable evidence of observed attacks against exploitation of this vulnerability”. CISA added it to its list of known exploited vulnerabilities the same day. The Security Update Guide still shows “Exploited: No” for this CVE, so a report filtered on that flag will miss it. If any SharePoint server lacks the August update, install it now.
  • Of the 21 new entries, 18 are critical cloud-side flaws in Azure, Microsoft 365 Copilot, Dataverse and Fabric, all marked “Customer action required: No”. Two are Edge flaws, and one is CVE-2026-96940 in Exchange Server, published on 2 October and covered below.

Microsoft has published no mitigations and no workarounds in the October release.

Windows lifecycle and enforcement updates

These support milestones passed with this release on 13 October, as scheduled:

The next milestones fall on 10 November 2026, the date of November’s Patch Tuesday. .NET 8 and .NET 9 reach the end of support, as do PowerShell 7.4 and 7.5. Windows 11 Enterprise and Education 23H2, and IoT Enterprise 23H2, reach the end of updates, and Microsoft says November’s update “will be the last update available for these editions”.

Microsoft also starts or tightens several enforcement changes with this release:

  • Windows 11 24H2, 25H2 and 26H2, and Windows Server 2025, now restrict NTLMv1-derived credentials for single sign-on by default. Where Credential Guard is off, Microsoft warns this “might affect Wi-Fi, Ethernet and VPN connections that use MS-CHAPv2-based authentication” (KB5066470).
  • AD FS Distributed Key Manager container permissions move into enforcement mode. Supported servers remediate automatically, but Server 2012 and 2012 R2 need manual remediation (KB5121391).
  • ReFS volumes on removable media enter an audit phase, and blocking is enabled by default from the January 2027 update (KB5130741).
  • The Windows Production PCA 2011 Secure Boot certificate, used to sign the Windows boot loader, expires on 19 October. Devices without its replacement, Windows UEFI CA 2023, keep starting and updating normally, but they stop receiving new early-boot protections (KB5062710).

Microsoft’s test guidance for this release runs to 496 Windows entries, 41 of them flagged as high risk, against 466 and 55 in September. Printing, scanning and font rendering account for 31 of the 41. The Readiness team recommends these testing priorities:

  • Printing. Print documents with mixed fonts from 32-bit and 64-bit applications to physical and virtual printers. Add network printers by discovery and by IP address, and print through a shared print server, a USB printer and a PostScript driver.
  • Downloaded files. The exploited Shell flaw bypasses Mark of the Web, so open files and shortcuts downloaded from the internet and confirm the SmartScreen and security warnings still appear.
  • Remote access. Test Remote Desktop with a non-admin account against hosts that have Administrator protection enabled, and test Wi-Fi and VPN connections that use MS-CHAPv2.
  • Application installs. Install, repair and uninstall a representative set of MSI packages, including packages with script custom actions. Windows Installer takes 38 fixes this month.
  • Network servers. Run DNS servers (52 fixes) and DHCP servers (18) under load, and confirm leases, zone transfers and conditional forwarders behave as before.

Each month, we break down the update cycle into product families, as defined by Microsoft, with the following groupings.

Browsers

For the third month in a row, Microsoft’s Patch Tuesday release lists no browser CVEs. Edge security fixes arrived between releases instead. Between 9 September and 12 October, Microsoft published 414 CVEs for Microsoft Edge in the Security Update Guide: 409 republished from Chromium and five specific to Edge. None carries an exploited flag, and no Edge release in that period reported an exploit in the wild.

Microsoft Windows

Windows takes 1,122 CVEs this month, 42 of them critical. Elevation of privilege accounts for 617 entries, information disclosure for 200 and remote code execution for 179. Of the 42 critical entries, 31 are remote code execution, nine are elevation of privilege and two are spoofing.

  • The exploited flaw is CVE-2026-96951, a Windows Shell security feature bypass that evades Mark of the Web defences. An attacker must convince a user to open a crafted file or follow a link. CISA added it to its list of known exploited vulnerabilities on 13 October, with a remediation date of 16 October.
  • DHCP takes 18 fixes, six of them critical remote code execution: five in DHCP Server and one in the DHCP client. DNS Server takes 52, 10 of them remote code execution, though none is critical. Critical remote code execution also affects Hyper-V, Message Queuing, Microsoft QUIC, the Remote Desktop Gateway, Windows Deployment Services, Active Directory Domain Services, NDES and the multicast transport driver.
  • In file and image handling, the Raw Image Extension has three critical fixes, one of them a CVE assigned by Cisco Talos, and the PostScript printer driver takes three more. Text shaping takes two, and Media Foundation, the codecs library, the video decoder, GDI+, the graphics component and the Windows PDF component take one each.
  • The virtualisation-based security enclave takes eight fixes, five of them critical elevation of privilege.
  • The most-patched areas are DNS Server at 52, Win32k at 48, the Windows Kernel at 46 and Windows Installer at 38.

Add this Windows update to your Patch Now schedule. Every client needs the fix for the exploited Shell flaw, and DHCP servers and Hyper-V hosts need the critical server-side fixes.

Microsoft Office

Microsoft released 180 Office CVEs this month, 26 of them critical, and remote code execution accounts for 107.

  • Client updates on Windows are Click-to-Run only, for Microsoft 365 Apps, Office LTSC 2021 and Office LTSC 2024. Office for Mac updates ship in the same release this month, rather than nine days later as they did in September. Excel takes 69 fixes, 11 of them critical. Word takes 22, Access 13, Outlook 10 with five critical, PowerPoint nine with four critical, and Visio three, all critical.
  • SharePoint Server Subscription Edition takes 34 CVEs in KB5002927, two of them critical. SharePoint Server 2016 and 2019 left extended support on 14 July 2026, and two of this month’s flaws list them as affected with no update: CVE-2026-69943 for both versions and CVE-2026-97783 for 2019.
  • Office Online Server takes 43 CVEs in KB5002928. Skype for Business Server takes three, in KB5132779 for 2015 CU13, KB5131693 for 2019 CU8 and KB5131692 for Subscription Edition CU1.

Add these updates to your Patch Now schedule, because 25 of the 26 critical entries affect Excel, Outlook, PowerPoint, Visio and Word.

Microsoft Exchange and SQL Server

Exchange has one critical entry this month and SQL Server has none.

  • Exchange Server has seven CVEs across 2016 CU23, 2019 CU14 and CU15, and Subscription Edition: one critical remote code execution, CVE-2026-70571, five elevations of privilege and one spoofing flaw. Six are fixed by the 13 October updates: KB5128895 for Subscription Edition, KB5128896 for 2019 CU15, KB5128897 for 2019 CU14 and KB5128898 for 2016 CU23.
  • The seventh, CVE-2026-96940, was published on 2 October. Microsoft lists it against a separate set of updates released that day, KB5129955 to KB5129958, not against the 13 October updates, so confirm both sets are installed. Microsoft rates both CVE-2026-96940 and the critical entry as “Exploitation More Likely”..
  • SQL Server has 22 CVEs, none of them critical: eight remote code execution, seven elevation of privilege, four information disclosure and three denials of service. Each supported branch gets a cumulative update and a GDR: 2025 (KB5126967, KB5128492), 2022 (KB5126934, KB5128493), 2019 (KB5128494, KB5128495) and 2017 (KB5128496, KB5128497).

Exchange goes on the Patch Now list. SQL Server goes on the Schedule list because none of its 22 entries is critical. If September’s SQL Server update is still outstanding, install it first.

Microsoft Developer Tools

Microsoft released 66 CVEs across its developer tooling this month: two critical, 63 important and one moderate. Remote code execution accounts for 18 entries and elevation of privilege for 13.

  • Both critical entries also affect Windows. CVE-2026-105016 is a remote code execution flaw in Microsoft QUIC that needs no authentication or user interaction, and it affects .NET 8, 9, 10 and 11 on Windows and Visual Studio 2022 and 2026. CVE-2026-96222 is an AD FS certificate validation flaw that Microsoft lists against both the .NET Framework and Windows Server.
  • Two entries were publicly disclosed before release. CVE-2026-108398 in the .NET Framework lets an authenticated attacker bypass Windows Defender Application Control. CVE-2026-92707, a denial-of-service vulnerability in the MessagePack-CSharp library assigned by GitHub, affects Visual Studio and the ASP.NET Core SignalR MessagePack protocol.
  • Visual Studio Code has 10 fixes, five of them security feature bypasses, and PowerShell 7.4, 7.5 and 7.6 take two.

Add these updates to your Patch Now schedule, starting with the .NET updates that carry the QUIC fix.

Adobe (and third-party updates)

Adobe published 11 security bulletins on 13 October, covering 175 CVEs across ColdFusion, Experience Manager, Commerce, Photoshop, Bridge, FrameMaker, Dimension, the Substance 3D tools and the Content Credentials SDK. None is rated priority 1, and Adobe is not aware of exploits for any of them. No Acrobat or Reader security update for this month. I mentioned last month that we are in for a few months of extraordinary patch releases. Harking back to 2003 (when I started work on the nascent field of Microsoft patch management), with Microsoft releasing just  51 updates, anything over a 1000, much less 1400 CVE entries would have been unimaginable. I don’t think that we are at a “patch maximum” yet — but I hope that things calm down soon.

  •  

Microsoft’s Patch Tuesday updates: Keeping up with the latest fixes

Long before Taco Tuesday became part of the pop-culture vernacular, Tuesdays were synonymous with security — and for anyone in the tech world, they still are.  Patch Tuesday, as you most likely know, refers to the day each month when Microsoft releases security updates and patches for its software products — everything from Windows to Office to SQL Server, developer tools to browsers.

The practice, which happens on the second Tuesday of the month, was initiated to streamline the patch distribution process and make it easier for users and IT system administrators to manage updates. Like tacos, Patch Tuesday is here to stay.

Patch Tuesday coverage has long been a staple of Computerworld’s commitment to provide critical information to the IT industry. That’s why we’ve gathered together this collection of recent patches, a rolling list we’ll keep updated each month.

In case you missed a recent Patch Tuesday announcement, here are the latest six months of updates.

October Patch Tuesday: 1,408 CVEs, 1 exploited flaw and a SharePoint surprise

Microsoft just shipped 1,408 vulnerabilities in one month, and a SharePoint flaw it marked “not exploited” is actually under attack right now. Our expert recommends a Patch Now scheduling for Windows, Office, Exchange and the developer tooling, and a standard release schedule for SQL Server.

Get more info on the October 2026 Microsoft security updates.

September Patch Tuesday: 963 CVEs, 2 exploited flaws, 1 message

September’s Patch Tuesday is Microsoft’s biggest of 2026, with 963 CVEs, two exploited flaws and a clear message: prioritize Windows, Office and SQL Server.

Two vulnerabilities are already exploited: CVE-2026-81963 in the Windows Update Stack and CVE-2026-85880 in Advanced Local Procedure Call. Nothing in this release was publicly disclosed ahead of the patch. Readiness recommends a Patch Now scheduling for Windows, Office, SQL Server and the developer tooling, and standard patch release for Exchange.

Get more info on the September 2026 Microsoft security updates.

August’s Patch Tuesday is a monster: 751 fixes, with an exploited Windows flaw

Microsoft’s August 2026 Patch Tuesday closes at 751 CVE entries (across all product families), with 108 rated as critical. One flaw is already exploited, CVE-2026-68820, an elevation of privilege in the Windows WinSock driver (afd.sys). Two more were disclosed but not exploited.

This security-only release earns Patch Now for Windows, Office and Exchange; no SQL Server updates this month. Unfortunately, several critical issues affect server roles: Windows DNS Server carries a cluster of critical RCEs; Windows DHCP Server is the most-populated Microsoft product family at 14 entries. Testing should lead with printing and fonts and the Remote Desktop client, then a WinSock smoke test given the exploited afd.sys flaw.

Get more info on the August 2026 Microsoft security updates.

July’s Patch Tuesday sees an end-of-support collision amidst a massive, record-setting patch wave

Microsoft addressed 722 CVEs this month once the 427 Chromium upstream relays are set aside — roughly three times a normal cycle and one of the largest single months in recent memory. Two vulnerabilities arrive under active exploitation: an elevation of privilege in Active Directory Federation Services (CVE-2026-56155), and an elevation of privilege in SharePoint Server (CVE-2026-56164). A third, a BitLocker security feature bypass (CVE-2026-50661) is publicly disclosed but not yet exploited.

The July 2026 Patch Tuesday earns Patch Now recommendations for Windows, Office, Exchange, and SQL Server. SharePoint has two critical RCEs on top of its exploited zero-day, and Exchange Server returns with a critical on-premises spoofing flaw. Adding to our (dear) administrator’s efforts, SharePoint Server 2016/2019 and SQL Server 2016 all reach end of support today.

More info is available here on Microsoft Security updates for July 2026.

For June, Patch Tuesday means an IT scramble

Microsoft this month released 206 updates affecting Windows, Office, Exchange Server, and its developer tools — including three Windows vulnerabilities already publicly disclosed. That trio includes an elevation of privilege in the Collaborative Translation Framework (CVE-2026-45586), a denial of service in HTTP.sys (CVE-2026-49160), and a BitLocker security feature bypass (CVE-2026-50507). At the moment, none appear to be under active exploitation, but all three are rated “Exploitation More Likely.” 

Even without an exploited zero-day, the June 2026 Patch Tuesday release requires Patch Now recommendations for Windows, Office, and Exchange. The latter is back in the patch picture with a consolidated security update that Microsoft recommends installing “as soon as possible.”

More info is available here on Microsoft Security updates for June 2026.

For May, Patch Tuesday means 139 updates — but no zero-days

Microsoft this month released 139 updates affecting Windows, Office, .NET, and SQL Server (though there were no updates for Microsoft Exchange Server). Despite the absence of zero-days, the May Patch Tuesday update still requires Patch Now recommendations for Windows and Office. 

The combination of three unauthenticated network RCEs (Netlogon, DNS Client, and SSO Plugin for Jira and Confluence), four Word Preview Pane RCEs, the large TCP/IP vulnerability cluster, and the carry-over BitLocker recovery condition (still active on Windows 10 and Windows Server) warrants an accelerated deployment release schedule. 

More info is available here on Microsoft Security updates for May 2026.

  •  

Astronomers Get a Better Look at a Rare White Dwarf–Brown Dwarf Pair

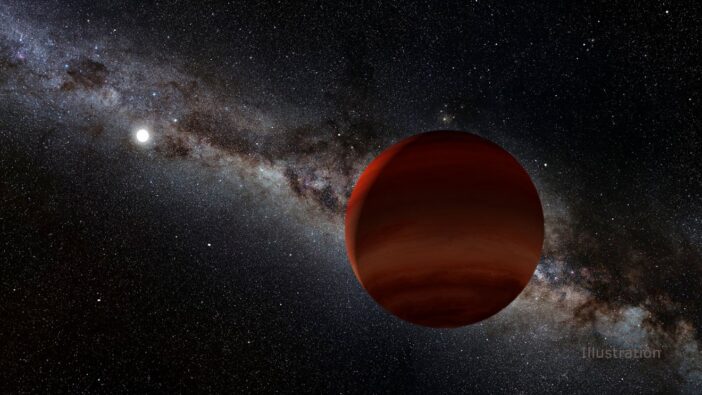
Illustration of a brown dwarf orbiting a white dwarf

Researchers have followed up on the discovery of a rare binary system containing a white dwarf and a brown dwarf. This unusual pairing offers valuable insights into the physics of atmospheres subjected to strong radiation.

Odd Couple

In 2025, researchers searching through observations from the Transiting Exoplanet Survey Satellite (TESS) spotted an eclipsing binary system in which a brown dwarf orbits the white dwarf J0404+1112 every 2.93 hours. Only about a dozen white dwarf–brown dwarf binaries have been confirmed so far, and each newfound system offers clues to how substellar or planetary companions survive a star’s transition from main-sequence star to swollen red giant to blazing white dwarf.

Because the two objects orbit one another so closely, this remarkable system also offers researchers an opportunity to study the dynamics and chemistry of an atmosphere blasted with high-energy radiation, with important implications for close-in brown dwarfs and giant planets.

Insights from New Observations

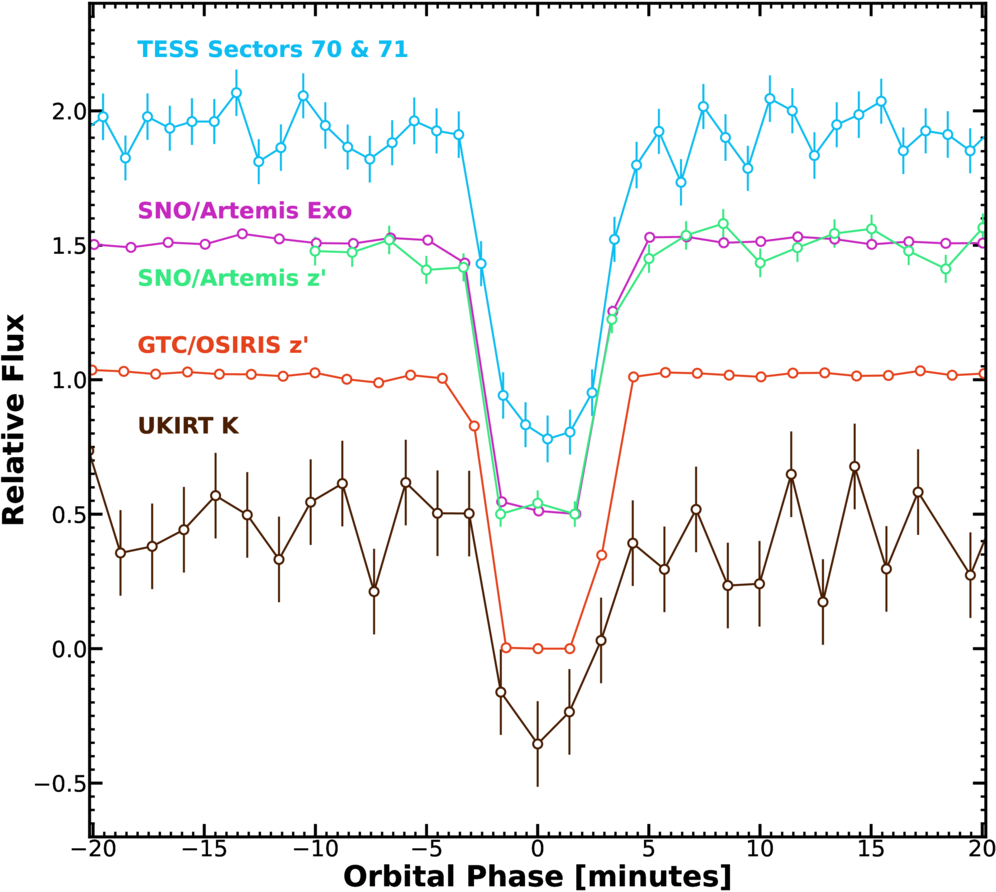
eclipse photometry of J0404+1112

Eclipse photometry of J0404+1112 from TESS, SPECULOOS, the Gran Telescopio Canarias, and the United Kingdom Infra-Red Telescope. [de Wit et al. 2026]

Based on early data from TESS and SPECULOOS, Julien de Wit (Massachusetts Institute of Technology) and collaborators posited that the J0404+1112 system contained an unusually puffy low-mass white dwarf and a 25-Jupiter-mass brown dwarf. However, the initial data couldn’t fully constrain the white dwarf’s properties, leaving degeneracies between its temperature, radius, and other factors.

Now, the team has obtained new photometry from the Gran Telescopio Canarias and the United Kingdom Infra-Red Telescope, plus spectroscopy from the Gran Telescopio Canarias, to get a better sense of the system. These observations allowed them to break the degeneracies in the white dwarf’s properties, showing it to be an 0.60-solar-mass white dwarf that has been cooling for more than 10 million years to a present-day temperature of 28,000K. The brown dwarf also appears to be more massive than initially thought, weighing in at roughly 40 Jupiter masses.

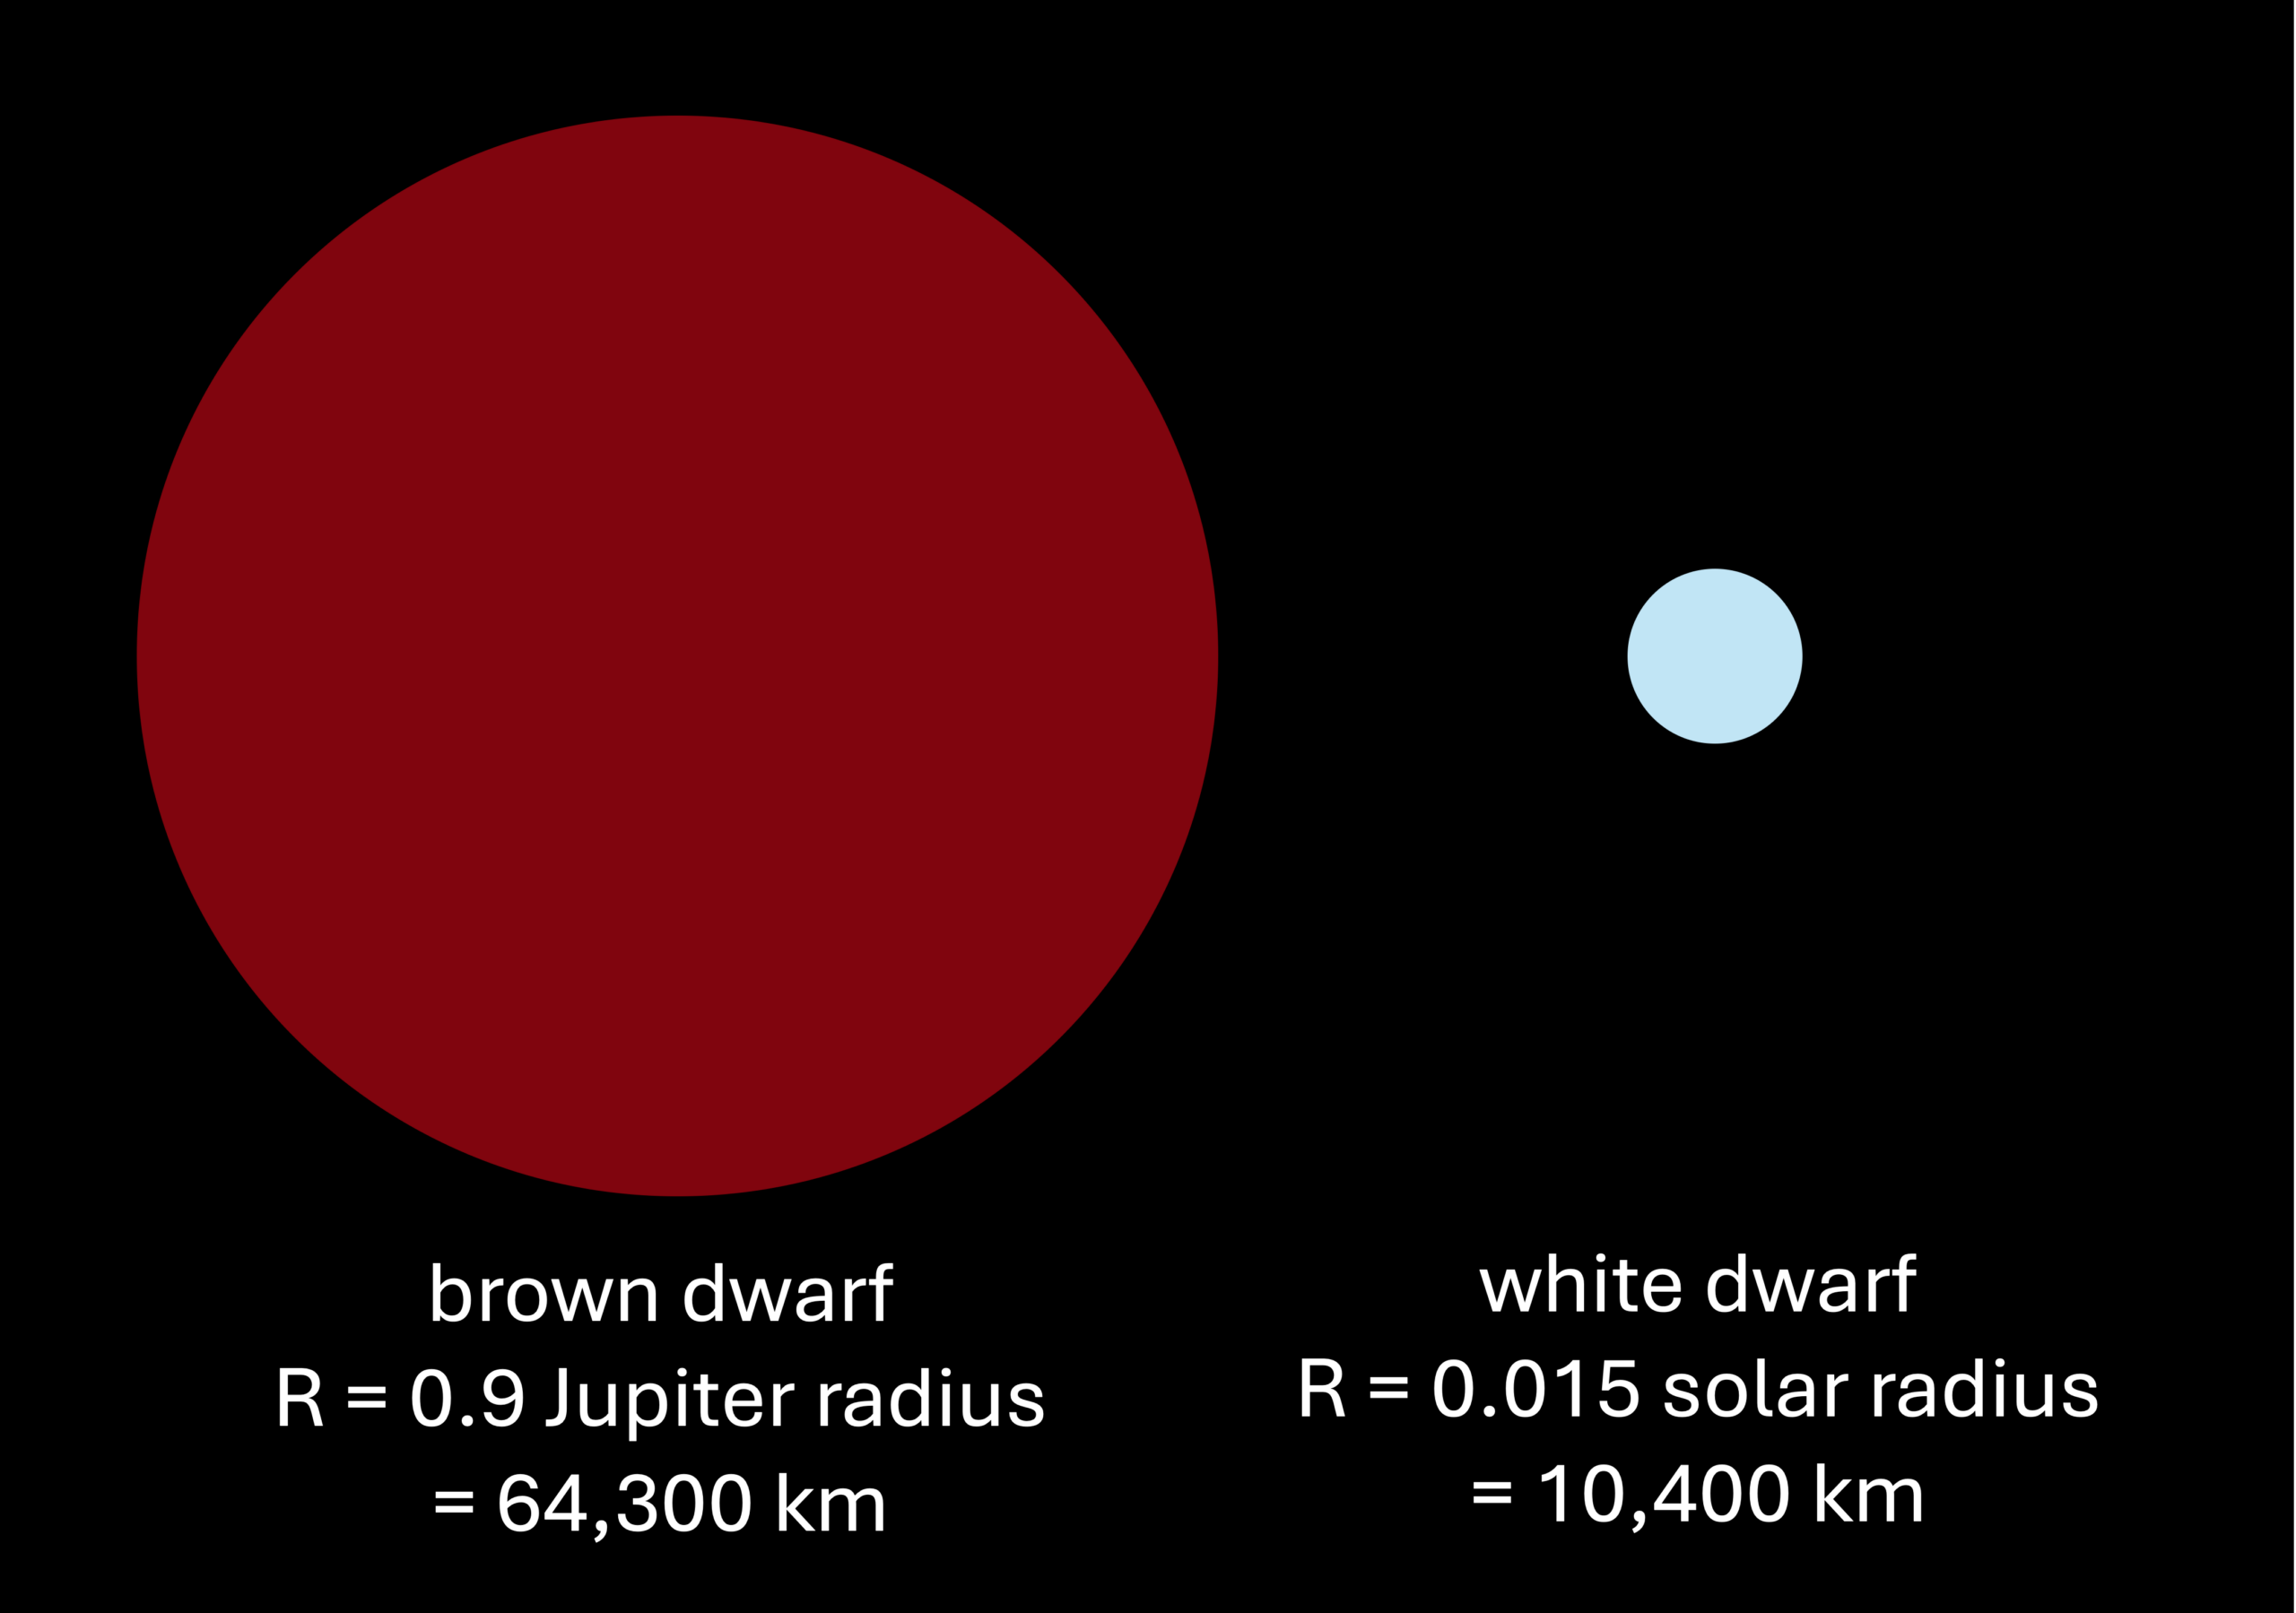
diagram illustrating the relative sizes of J0404+1112 and its companion brown dwarf

This diagram shows the relative sizes of the brown dwarf and the white dwarf. [AAS Nova/Kerry Hensley]

Like Night and Day

Because the system’s orbit is almost exactly edge on from our point of view, the white dwarf is completely eclipsed as the much larger brown dwarf passes in front of it. This allows the contributions from the two components to be separated, and for the emission from the brown dwarf’s nightside to be measured. The authors constrained the brown dwarf’s nightside temperature to roughly 1750K. Its dayside temperatures are likely to be significantly higher — potentially around 3750K at the point where the white dwarf is directly overhead — but more data are needed to constrain the dayside temperature of this world.

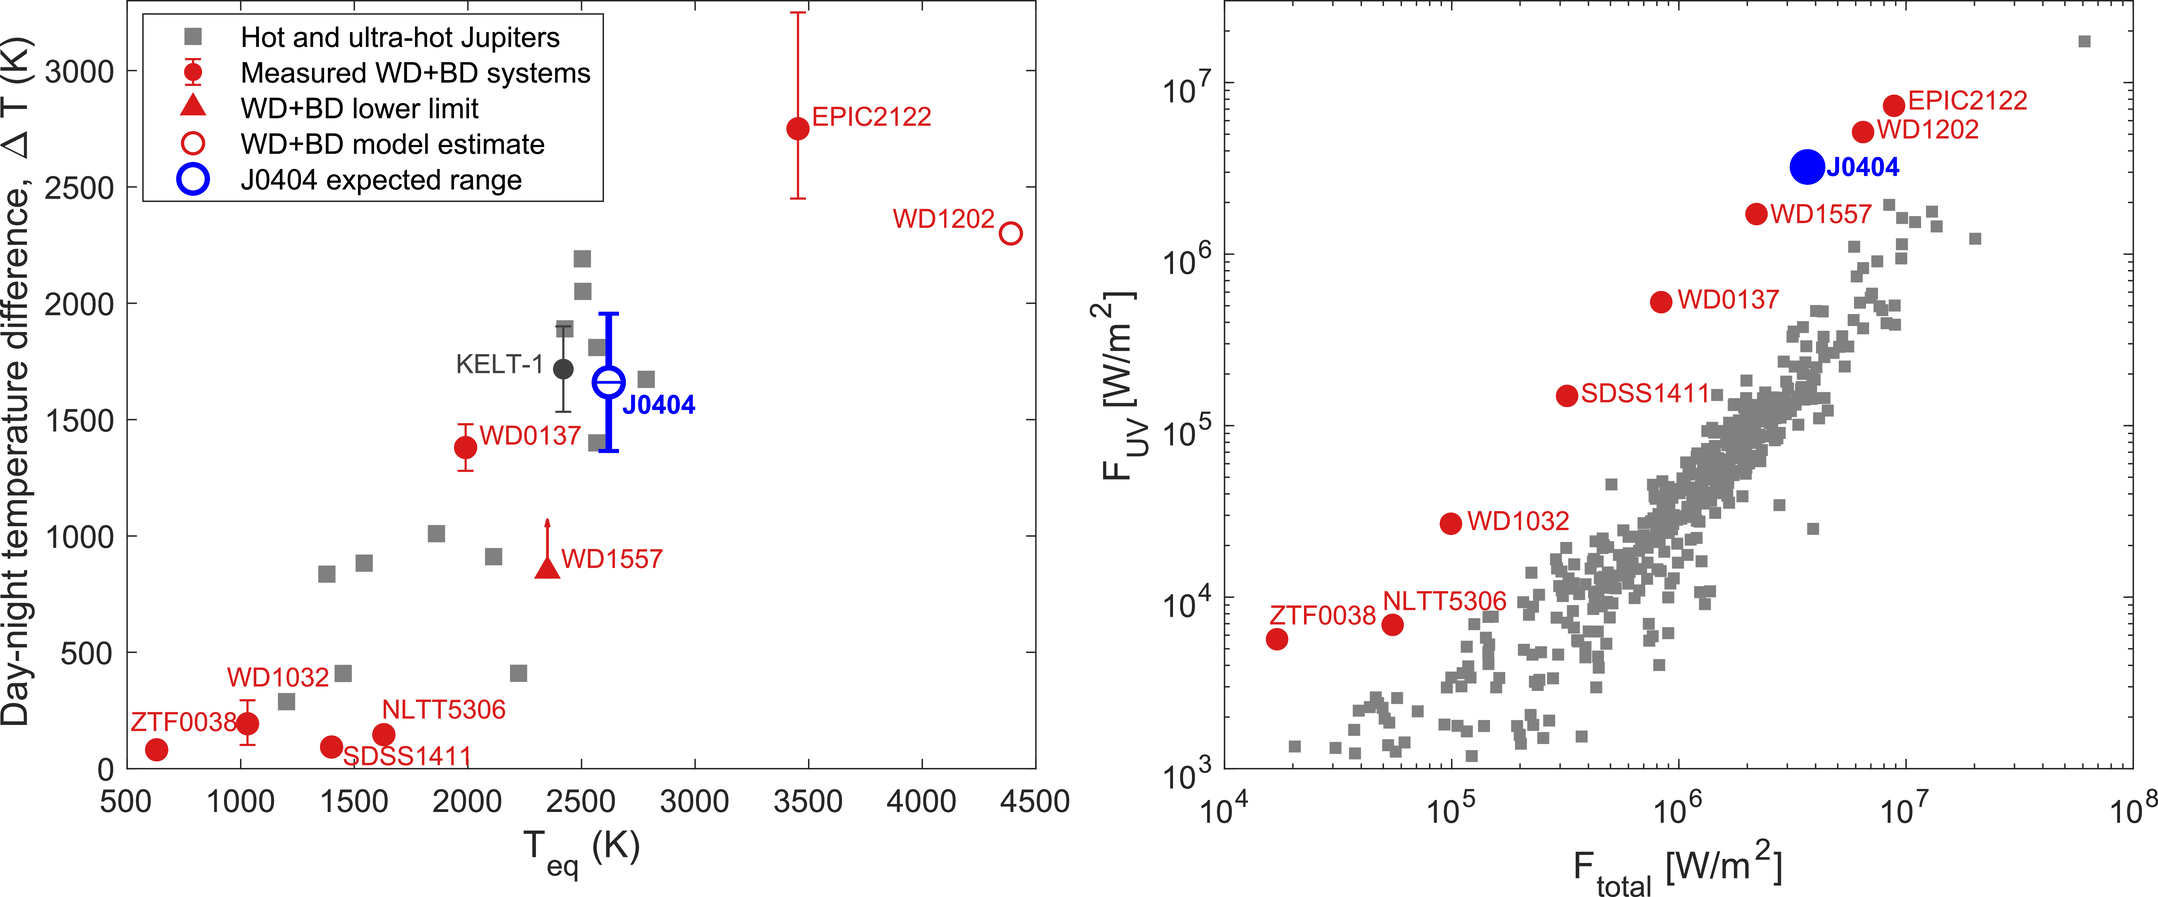
comparison of day–night temperature difference and irradiation flux of J0404+1112 compared to other systems

Day–night temperature difference (left) and irradiation flux (right) of the brown dwarf in this system compared to other white dwarf–brown dwarf systems and hot and ultra-hot Jupiters. Click to enlarge. [de Wit et al. 2026]

The estimated day–night temperature difference for this brown dwarf places it in the realm of hot and ultra-hot Jupiters. However, it’s subjected to more ultraviolet radiation than a typical hot or ultra-hot Jupiter orbiting a main-sequence star. This makes J0404+1112 a valuable system for disentangling the interconnected effects of temperature, radiation environment, atmospheric composition, and other factors on hot or ultra-hot Jupiters and other strongly irradiated brown dwarfs. We can certainly expect to learn more about this rare system as new data are collected!

Citation

“J0404+1112: A 3 hr Eclipsing White Dwarf–Brown Dwarf Probing Multiple Atmospheric Regimes,” J. de Wit et al 2026 ApJL 1009 L40. doi:10.3847/2041-8213/ae9a97

The post Astronomers Get a Better Look at a Rare White Dwarf–Brown Dwarf Pair appeared first on AAS Nova.

  •  

Planets Scattering Planets in Warm Jupiter Systems

exoplanet system with three planets

While our solar system sports one Jupiter-like planet, exoplanet discoveries have revealed that giant planets come in a few different forms in systems with varying architectures. A recent study has explored how the mass–eccentricity relationship in warm Jupiters is shaped by dynamical interactions between planets.

Jupiter-like Planet Eccentricities

Exoplanet surveys have uncovered three different Jupiter-like planet populations across the galaxy: hot, warm, and cold Jupiters. Much like our own, cold Jupiters orbit on long periods, far away from their host stars. Conversely, hot Jupiters zip around their host stars on extremely short-period orbits. Somewhere in between, warm Jupiters orbit their host stars with periods from 10 to 365 days.

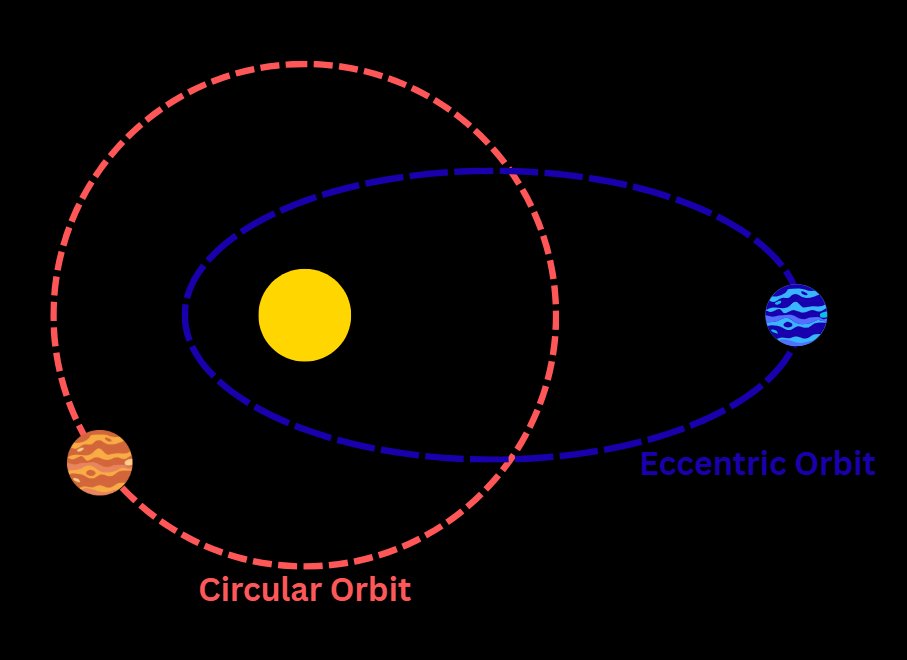
eccentric and circular orbits

Diagram showing examples of a circular and an eccentric orbit. Click to enlarge. [AAS Nova/Lexi Gault]

These giant planets have proven to be deeply entwined with the makeup of their host systems, and their orbital properties have been used to test and trace planet formation pathways. For example, long-period cold Jupiters discovered in radial velocity surveys have exhibited a positive correlation between planetary mass and orbital eccentricity. This mass–eccentricity relationship, as previous studies have suggested, is likely the result of a process known as planet–planet scattering, in which dynamical interactions between planets in the same system cause significant and chaotic changes to their orbits.

Does this relationship extend to shorter-period giant planets as well? Hot Jupiters are heavily impacted by tidal interactions with their host stars, circularizing their orbits and erasing dynamical imprints on their eccentricities. Warm Jupiters, on the other hand, orbit far enough away for their eccentricities to preserve clues about their energetic histories. Recently, thanks to the Transiting Exoplanet Survey Satellite (TESS), astronomers have identified a positive correlation between planetary mass and eccentricity in a growing sample of warm Jupiters, but the exact driver of this trend has yet to be uncovered.

Planets Scattering Planets

To test if the positive mass–eccentricity correlation in warm Jupiters is consistent with planet–planet scattering, Jiayin Dong (University of Illinois at Urbana-Champaign) constructed a sample of 85 warm Jupiters from the NASA Exoplanet Archive. This carefully selected sample, dominated by discoveries from TESS and Kepler, included planets with masses between 0.3 and 15 Jupiter masses and orbital periods between 10 and 365 days. In conjunction with this sample, the authors built a planet–planet scattering framework to assess the range of properties anticipated for scattered warm Jupiter systems.

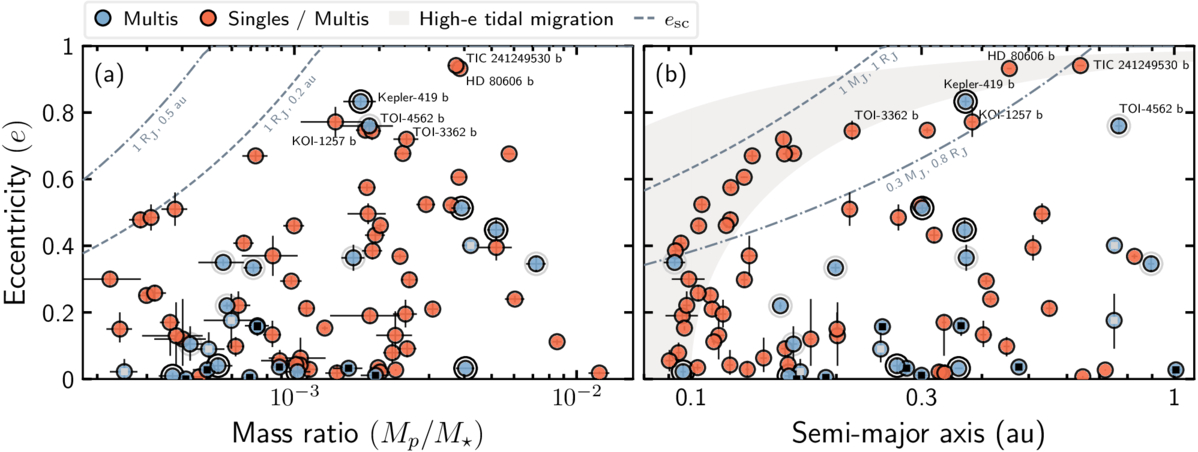
Eccentricity planet-star mass ratio and semimajor axis

Warm Jupiter eccentricity versus planet–star mass ratio (left) and semimajor axis (right). Click to enlarge. [Dong et al 2026]

Comparing the observed trends in their sample with their theory-based expectations, Dong and team showed that planet–planet scattering naturally explains the mass–eccentricity relation of warm Jupiters. In their framework, warm Jupiters originate in compact, multiplanet systems, and as the systems evolve, gravitational interactions between planets excite orbital eccentricities and inclinations, leading to close encounters. These encounters can cause planets to collide or to be ejected from the system entirely.

The mass–eccentricity relation of warm Jupiters, the authors suggested, represents a transition from collision-dominated interactions among low-mass planets to ejection-dominated interactions among high-mass planets. For massive enough systems, scattering can excite eccentricities high enough to trigger the high-eccentricity migration responsible for moving hot Jupiters to their close-in orbits. Overall, this study suggests that warm Jupiters are not a distinct planet species, but instead may represent the shorter-period counterparts of cold Jupiters whose orbits are shaped by the same dynamical processes. Future observations expanding the sample of warm Jupiters and discoveries of additional planet companions will further uncover the links between hot, warm, and cold Jupiter systems.

Citation

“Planet–Planet Scattering Explains the Mass–Eccentricity Relation of Warm Jupiters,” Jiayin Dong et al 2026 ApJL 1007 L29. doi:10.3847/2041-8213/ae930e

The post Planets Scattering Planets in Warm Jupiter Systems appeared first on AAS Nova.

  •  
❌