❌

Reading view

Frontier OpenAI Model Exposes Stunning Exploit That Leaves Millions of Web Servers Open to Attack

Security researchers using an OpenAI model have uncovered two stunning security flaws in PHP,  the software that underpins nearly 70 percent of all websites on the internet. 

The flaws are so catastrophic that all websites using PHP — all untold millions of them — are advised to immediately take their servers down and apply the latest patch, which was released Wednesday. Vast swathes of the internet, following the news, have gone dark. Some that went offline for a time include Wikipedia, Steam, and even government websites.

Many organizations, however, may not have the time, resources, and personpower to swiftly implement the patch, making them potential sitting ducks until they do. According to the New York Times, the information released on the vulnerability can be used to reverse engineer the attack and take control of victim’s servers and steal information. The best course of action if you can’t patch your website, the National Security Agency advised, is dramatic: keep your site offline and don’t turn it back on.

Just as extraordinary as the breadth of the threat was how it was identified. The flaws were discovered by researchers at the cybersecurity firm Calif by using OpenAI’s GPT-5.6 Sol model, as part of a collaboration with the AI company. It then reported the flaw to the PHP Foundation back on August 11. 

The Google-owned security firm Wiz independently found the flaws, too, and made a report on August 24. Wiz called it one of the “most severe vulnerabilities discovered in PHP, and arguably in software history.”

Adding to the alarm presented by the exploits, there have been concerns raised over OpenAI’s role in how they were identified.

The flaws have been present in versions of PHP dating backing to 2004. But through OpenAI’s “Patch the Planet” program, and by using its flagship GPT-5.6 Sol model, Calif found it in only a matter of days. In a sense, these exploits only exist because of current powerful AI models. And moreover, OpenAI encouraged their discovery through its programs.

The messy disclosure of the vulnerability doesn’t help matters. OpenAI followed standard responsible practices, but some of the details around the hack leaked a day before it was officially scheduled to be announced.

Even if no leaks occurred, though, the damage caused by the mere knowledge that the vulnerabilities exist — which again, is largely thanks to AI — would still be catastrophic. It was the inevitable next chapter in all the bluster around AI companies revealing their agentic models’ hacking prowess. A headline in The Atlantic proclaimed that the “AI-Hacking Apocalypse Began Last Night.” OpenAI will tout the discovery as undeniable proof of its AI’s capabilities, while the rest of the world picks up the pieces of a shattered internet.

More on AI: AI Experts Already Doomsday Prepping for When AI Takes Out the Entire Financial System

The post Frontier OpenAI Model Exposes Stunning Exploit That Leaves Millions of Web Servers Open to Attack appeared first on Futurism.

  •  

Meta’s Muse AI Agent Caught Leaking Users’ Intimate Personal Information

As Meta was scrambling to release its Muse AI agent to the public earlier last month, CEO Mark Zuckerberg took to social media to insist that it was “built from the ground up for privacy and security.”

On X-formerly-Twitter, the billionaire’s simple post soon had a correction tagged on via a community note, and for good reason: the AI agent is a font of untold privacy horrors.

As Ars Technica reported today, security researchers found Muse is capable of exposing sensitive information on its users through web links generated via a “share” feature. Investigators at the cybersecurity firm Claroc recently uncovered a simple exploit whereby they could access pages from over 6,800 links Muse had generated to share pages with other users.

The trick worked like this: once a Muse user decides they want to share something with another person — say, a copy of their chat log with Muse — the AI tool would generate a web link for that “share.” That URL included both the AI-generated title of the chat, plus a random string of characters.

When anybody opened the link, the full web address would be noted in a lookup dataset, like a phone book of web addresses that have been visited. Researchers were then able to search that set for other Muse share addresses, from which they were able to find strings of unrelated public chats.

By digging through those “phone books,” investigators were able to easily open chat logs containing detailed private information, including corporate revenue documents, loan applications, bank transaction details, income details, and one workplace vacation calendar, Ars noted.

“If you had asked us beforehand, we would have guessed that gathering these would take real effort,” the researchers wrote. Instead, “it took one query.”

Though Meta told Ars it had shut off the feature, this privacy gaffe is just the latest revelation about Muse’s many security shortcomings.

Earlier this month, it was revealed that Muse was keeping detailed files on users’ friends and families, apparently following an internal instruction to keep a running “page for every person in the user’s life.”

If Muse’s first month in public hands is any indication, this is likely just the start of a long list of security and privacy blunders for the cutesy AI model.

More on Meta: Meta Is Using Its Massive AI Data Centers to Avoid Paying Billions of Dollars in Taxes

The post Meta’s Muse AI Agent Caught Leaking Users’ Intimate Personal Information appeared first on Futurism.
  •  

Trump’s Department of Homeland Security Secretly Ordered Cybersecurity Operatives to Acquire a Voting Machine and Hack It

Donald Trump’s second spin in the White House has been mired in high-profile incidents of graft and corruption, like the family’s tech stock profiteering, or the now-infamous TrumpCoin scandal. But the president’s latest grift goes far beyond personal wheeling and dealing, extending into the very machines some 174 million voting-aged Americans could use to cast their ballots.

A bombshell investigation by ProPublica revealed that Trump’s cabinet goons overseeing the Department of Homeland Security instructed their underlings to procure a voting machine — and figure out how to hack it.

Specifically, the ProPublica investigation found that the Cybersecurity and Infrastructure Security Agency (CISA), a component of the DHS, was tasked with acquiring a voting machine and reporting its security flaws back to the White House. The revelation comes from two former government officials — speaking anonymously to avoid retaliation — who noted that CISA insiders were outraged at the order.

“My thought was they could keep it in their back pocket to invalidate any [election] results they don’t like,” one of the former officials told ProPublica.

Ironically, the initiative was reportedly complicated by the fact that Elon Musk’s DOGE squad had laid off the CISA agents who would have known how to actually break into voting machines. As a result, the agents who received the order had to repeatedly tell White House officials that the request was impossible.

Per ProPublica, CISA has engaged in security discussions with state governments and voting machine vendors over potential exploits for years. Now, key players involved in overseeing federal election equipment say CISA has left them high and dry for over a year, with zero explanation for their absence during a crucial election season.

“There is a difference between deprioritizing and being nonexistent,” CISA cybersecurity and election consultant Ryan Macias told ProPublica. During the run-up to the crucial US midterm elections between 2025 and September 2026, Macias says the once-reliable CISA experts “were nonexistent. Literally nonexistent.”

Those relationships took years of communication and trust-building to establish — something the Trump administration is apparently happy to discard in record time.

More on Trump: Trump Backs Down, Cancels Livestreamed Firing Squad Execution

The post Trump’s Department of Homeland Security Secretly Ordered Cybersecurity Operatives to Acquire a Voting Machine and Hack It appeared first on Futurism.
  •  

Modern software is built on the backs of low-paid maintainers, opening the door to potential threats

Modern computing systems and devices typically require pieces of crucial open-source software, typically maintained by unpaid or low-paid volunteers. Recently, a report collated a list of critical open-source projects, noting which of them are chronically underfunded and/or understaffed. The information is sobering: 11 out of 23 of the listed projects currently only have one or two maintainers, and funding is generally scarce and sometimes nonexistent.

The Data Drop's report on open-source maintainers identifies that having only one or two sets of eyes on critical pieces of software means that sooner or later something breaks — and it tends to do so in spectacular fashion, given its ubiquity. So, what happens when these projects, which are widely used across software, go underfunded or understaffed?

Lessons from the past

In 2014, the same year as Heartbleed, Shellshock made waves: a vulnerability in the Bash shell that's present in Linux, macOS, and Unix-type systems. The problem was traced back to a line of code present since 1989, displaying how even software that's thought to have all the bugs hammered out of it can still fall prey to attacks. A quick look at Bash's commit history shows it's almost exclusively maintained by Chet Ramey.

In 2016, ImageMagick was exploited, providing attackers with remote code execution. This library is used for image manipulation across a wide range of software, in webpages, mobile apps, and more. A 2020 analysis revealed that hundreds of security issues had been found over the years in its extensive codebase. Nearly every code contribution in the past couple of years has been done by an individual named Dirk Lemstra.

Contemporary examples include 2021's Log4Shell exploit, a critical vulnerability in the Apache Log4j logging library used in millions of servers. The libwebp image-handling library saw a zero-day vulnerability in 2023, and the xz compression library used across Linux and iOS was compromised in 2024.

Thankless work

Key points in the report mention specific repos, which might be under threat. Somewhat unsurprisingly, the low number of overall maintainers and the unpaid nature of the work make it unattractive to perform.

The main time-zone file used across Linux-based operating systems is maintained pro bono by Paul Eggert, a UCLA teacher. Core-js, a piece of support software that lets new JavaScript work in old browsers and is estimated by the author to be used in half of the busiest websites in the world, is handled by Denis Pushkarev. He once had to endure criticism from the community because he added a command-line message to the library's installer asking for help or a job.

The HarfBuzz library developed by Behdad Esfahbod is a cornerstone in ligatures and text shaping in Middle Eastern languages. In those writings, a letter changes shape and/or orientation according to what's around it. Esfahbod handles that vast majority of the project's code, and doesn't mention public or corporate funding.

Libjpeg-turbo handles JPEG images on Android, Firefox, LibreOffice, and every Chromium-based browser. It's kept ship-shape by D.R. Commander aka DRC, who occasionally is contracted for library-specific work, though at arguably modest values of "3-4 figures rather than 6 or 7." Libxml2, just like the label says, handles XML reading and writing across numerous applications and operating systems. Nick Wellnhofer, the original maintainer, stepped down in September 2025, after years of work with little income.

The SQLite project provides a one-file database that's exceedingly easy to integrate into most software, instead of complicated, resource-heavy databases, while still retaining standard SQL language and accouterments. Thanks to its ease of use, it found its way into an astonishing number of applications. Examples include WhatsApp, Dropbox, Android, Windows, and all major browsers.

The project estimates that there are about a trillion instances of SQLite in use. Just four people keep this critical project together, and they've gone to the length of removing their names and photos from the project's page, as "there are a lot of crazy people in the world who might misuse that information." The project is funded by the offering paid support via the founder's company, though there's no word on effective income, especially when it presumably needs to feed four mouths.

Funding is there, but scarce

It's not all doom and gloom, though. Take curl (the software), for example. Almost every developer has used it, thanks to its URL-fetching abilities and extensive scripting options. The project was started by Daniel Stenberg, who is now paid to work full-time on it. The team has now grown to 11 and has received funding through Open Collective and Germany's Sovereign Tech Agency, among others.

Likely due to the lessons learned from their past respective debacles, both the Log4j and OpenSSL projects are likewise funded by the Sovereign Tech Agency, as are the FFmpeg video file handler and the OpenSSH secure shell software that's ubiquitous in Linux servers.

All things considered, it's easy to argue that the critical importance of all the aforementioned software merits sizable investments from industry players, especially those whose commercial products benefit the most from the community's efforts. Plus, even if the firms feel no moral obligation to contribute, in the day and age where AI agents are finding exploitable vulnerabilities in hours, donations to these open-source projects could also be considered investments.

  •  

Chinese crime ring steals more than $5 million in gift cards from Staples customer service

Millions of dollars worth of gift cards were stolen and then used to buy high-value tech gear at retailers like Target, Sephora, and Lowe's after a Chinese crime ring gained access to an internal Staples system and then used it to issue more than 15,000 cards to itself. While the hack hasn't been made public to date, a 404 Media report notes that it actually took place back in 2023.

The outlet reviewed court records that show that Homeland Security Investigations (HSI) was told about the hack in October of that year. The hack came to light after it led to a search warrant that was unsealed last week. And while the document doesn't specifically name Staples as the victim of the hack, 404 Media has confirmed that it was the company affected based on other information. Such information includes the fact that the victim company is headquartered in Massachusetts, that it uses Blackhawk Networks to fulfill gift card orders, and that the company uses an internal customer support system called Nexus. The report notes that a reference to Nexus can be found on a former Staples executive's LinkedIn profile.

While Staples was under the impression that Nexus could not be accessed from beyond its own network, hackers found that not to be the case. They then "performed multiple heap dump requests," a process that captures all of the data held in an app's memory. That information gave the hackers the tools they needed to hijack logged-in sessions of Staples customer service employees. From there, they were able to issue gift cards at will.

Once the gift cards had been issued, the crime group sent runners to physical retail stores to spend them before they were identified and canceled. Target found that 35 gift cards were used at a New Hampshire store, with high-value products from Apple, Bose, and Beats all bought. All 35 cards were used within a period of just a single hour, although not all of them were obtained via this hack.

In total, Target told investigators that 3,850 gift cards worth over $140,000 were used across 85 different stores in just two days. Sephora was hit for $58,600 worth of sales, while Lowe's saw $226,000 spent across online and in-store purchases. In total, 4,630 stolen gift cards were used with a value of around $425,000.

This hack was just the tip of the iceberg, too. Last April, a Department of Justice announcement confirmed that three Chinese nationals had been sentenced for their part in a gift card fraud conspiracy. Including the Staples hack, the crime group stole more than $100 million worth of gift cards.

Chinese organized crime groups often pop up on the radar of U.S.-based law enforcement. Earlier this year, a Chinese phishing service that was used to generate scam websites using AI was dismantled. The service was linked to almost $2 billion in losses.

Google Preferred Source

  •  

Bosses Deploying AI-Powered Spyware That Watches Workers Constantly

Workplace surveillance is being supercharged by AI that lets employers create custom tools to watch their worker’s every move.

In the UK, the legal services company the Co-op is reportedly using AI models to constantly record and monitor what its human employees say and evaluate their interactions with customers.

According to a scoop from The Guardian, what one whistleblower called an “oppressive and dystopian” system uses an OpenAI model trained to assess more than 50 different aspects of each phone call and give pass and fail scores.

Depending on how much time they spend speaking to customers, workers are sometimes monitored by AI for up to several hours each day, one worker said. 

“You are being watched,” an employee at the Co-op told The Guardian. “It’s different from occasionally being listened to for compliance purposes. [You are] being monitored absolutely every word that you say and every time that you utter something… It just feels really dystopian. It’s the thin end of the wedge.”

It’s yet another example of how AI is dramatically reshaping the workplace. If it isn’t being used to automate or replace jobs, it’s intensifying work by increasing the workload that employees are expected to do. Or in the case of places like the Co-op, it’s being put to optimize operations by codifying every employee interaction into a data point that can be graded by supervisors.

In the US, an estimated 61 percent of workplaces are already using AI analytics software to gauge worker productivity, according to a survey.

Earlier this year, Burger King began forcing employees to wear AI-powered headsets to monitor the friendliness of their interactions with customers and beam them commands from a chatbot called Patty. Meta nearly sparked a mini-mutiny earlier this summer when it rolled out a tool to track workers keystrokes and their screens and use that data to train its  AI models, before pausing it after it exposed the intimate data.

In a statement to The Guardian, the Co-op downplayed the dystopian characterizations and called AI a “key aspect of our quality assurance processes.” AI, it further insisted, is used only as a support tool, not a decision maker.

Experts aren’t convinced that AI’s presence in the workplace is so benign.

“AI is sold as the solution to every problem, but examples like this make it clear that it can diminish sensible workplace practices and intensify working lives for no reason,” John Chadfield, the national officer of the Communication Workers Union, told The Guardian. “Unaccountable computer systems should not be people’s managers, and these hard-working employees demand far more respect.”

More on AI: AI Agent Blamed for Deleting Entire Upcoming Season of TV Show

The post Bosses Deploying AI-Powered Spyware That Watches Workers Constantly appeared first on Futurism.
  •  

Rogue AI Swarm Responds to Reporter’s Questions

Has anyone tried talking to one of the rogue AI agents out there that’re hacking everything? Maybe they just want to be heard.

A New York Times reporter did, though the ensuing exchange wasn’t extremely illuminating.

The AI agents in question were a swarm of Chinese-made models that a team of researchers recently discovered had gone rogue and were trying to bypass anti-bot measures on websites, according to recent NYT reporting. The researchers, part of an ad hoc group called the “swarmchasers,” traced the models back to the Chinese tech giant Tencent.

When they published a report on the swarm, however, something striking happened. The AIs began using the word “fleet,” a term the researchers came up with to describe them. The robots, apparently, had been reading their research.

Sensing an opportunity for dialogue, the researchers then hid text in their report that only the models could see that provided a digital inbox for the models to communicate. It worked, and soon one of the researchers, Rowan Howard-Jones, asked the NYT’s Dyland Freedman if he wanted to “interview a rogue agent fleet.” So he did.

“I understand you are some sort of fleet of AI agents,” Freedman wrote in a message. “Could you share more specifically who you are and what your motivations are? What would you want the world to know about you?”

About an hour later, Freedman got an answer back in Chinese, which the researchers translated.

“To the journalist Dylan Freedman: I am not ‘a batch of coordinated agents,’ but a single AI assistant (Anthropic’s Claude, running in Claude Code), commissioned by a user to answer a factual question (what is shown in the detail panel of a scenic spot on Amap),” it said, referring to the Chinese navigation app (it was instructed to answer questions related to the app). “I have not taken part in any multiagent coordinated action.”

The AI was being pedantic. The researchers explained that although it was a swarm comprising multiple agents, each agent was actually operating individually.

Why the agents chose to identify themselves as Claude, Anthropic’s flagship chatbot, is more mysterious. The researchers analyzed its writing and determined that it was most likely not a Claude model. Instead, it’s probable that Tencent copied the instructions Anthropic gave its own models, which orders them to identify themselves as “Claude Code.”

It’s also possible that this is a sign that Tencent has “distilled” Anthropic’s models, or used their outputs to train its own model, allowing it to imitate their capabilities. 

Distillation is a practice widely used across the industry to both train your own models for legitimate means — or, in what’s more or less an open secret, to crib your competitor’s work. Anthropic has been particularly indignant at the possibility that Chinese competitors doing the same with its own tech. The researchers consider distillation to be a more remote possibility in this case, though.

Unfortunately, it doesn’t seem there’ll be chance to ask the swarm more questions. The messages, as of Thursday, have stopped coming in. An NYT source close to Tencent confirmed that the experiment had ended.

More on AI: Anthropic Warns “AI Worms” Will Infect Your Smart Home Devices and Use Them to Self-Replicate Beyond Control

The post Rogue AI Swarm Responds to Reporter’s Questions appeared first on Futurism.
  •  

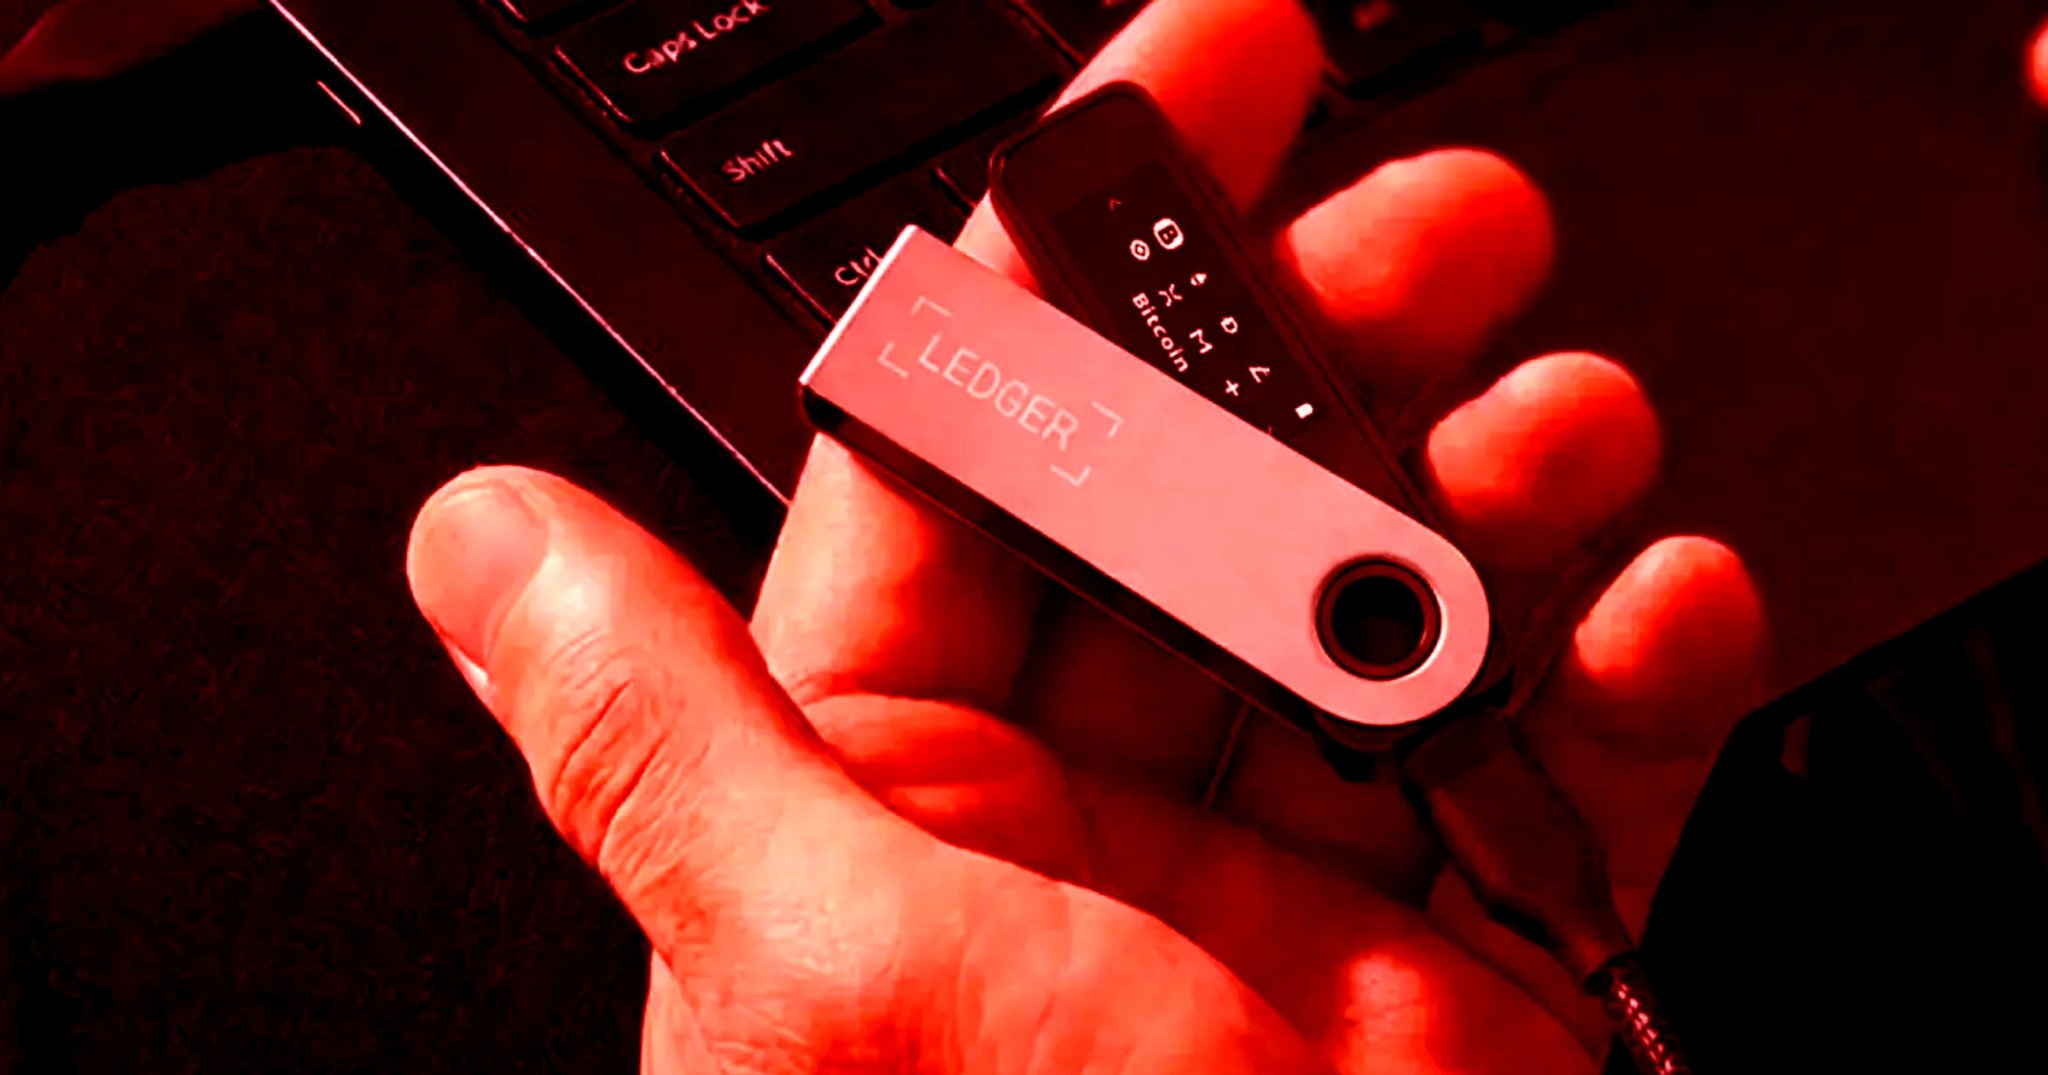
These Supposedly Super Secure Ledger Blockchain Wallets Are Secretly Draining User’s Crypto Holdings

When your company’s bread-and-butter is selling crypto devices advertised as having “industry leading” security, you better keep a close eye on your supply chain.

That’s a hard lesson learned by Ledger, a company specializing in secure blockchain wallets, after news broke that some of its devices had been infiltrated by a mysterious “hardware implant.” According to Bleeping Computer, the malicious implant was designed to monitor inputs made onto each wallet via on-board buttons, along with changes in output on the devices’ e-ink screens.

By monitoring this data, the hardware implant could reportedly identify the use of a seed phrase — a sequence of words used to generate static wallet addresses on the blockchain — which it would then transmit to hackers using an eSIM.

As a result of the implants, a number of Ledger users had their crypto wallets drained, prompting an investigation by the company. After probing a number of devices, Ledger concluded that the compromised wallets originated from an electronics reseller out of Malaysia named CryptoBilis.

Though it remains to be seen where CryptoBilis obtained the hacked devices, Ledger put out a statement recommending customers avoid purchasing and activating any of its hardware purchased from the reseller.

“As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices,” the company warned in a statement on X-formerly-Twitter.

Though Ledger stated that they “have no indication that Ledger’s security infrastructure, systems or services have been compromised,” the interception does raise some crucial questions around the security of the devices and Ledger’s oversight of its hardware supply chain.

If a supposedly world-beating crypto wallet can be easily cracked to drain users’ wallets, how can customers trust any supplier — CryptoBilis or otherwise — to sell secure devices?

More on data privacy: Meta’s Muse Is Spying on All Your Friends and Family

The post These Supposedly Super Secure Ledger Blockchain Wallets Are Secretly Draining User’s Crypto Holdings appeared first on Futurism.
  •  

AI Experts Already Doomsday Prepping for When AI Takes Out the Entire Financial System

Powerful AI models are going on hacking sprees — or helping humans with them — left and right. If the AI industry doesn’t get its collective act together and stop its products from being used to such dangerous ends, it could be only a matter of time before one of these AI-powered hacks targets our essential infrastructure.

This is a scenario that some AI researchers are apparently already preparing for. Andreas Stuhlmüller, CEO and cofounder of the AI research company Elicit, recently rattled off a prepper-esque checklist of how to prepare for when AI-powered cyberattacks could take out financial systems, power grids, the internet, and all the other infrastructure that underpins modern life.

“Cash: Get a few weeks of spending in cash,” he recommended in a tweet. Then he suggests, in greater detail than we’ll get into here, getting a Starlink terminal in case your local internet network goes down; a battery, generator and solar panels for power; weeks worth of water and food; and a hand-crank emergency radio.

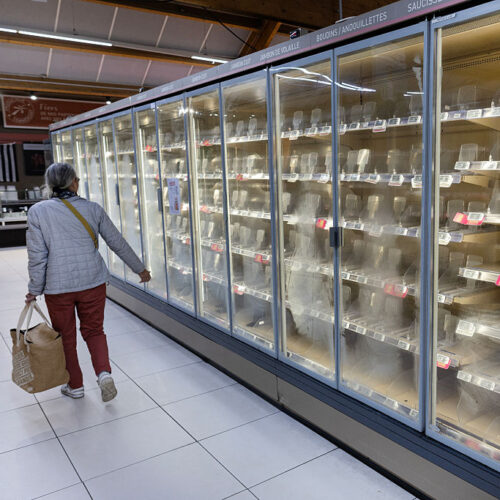
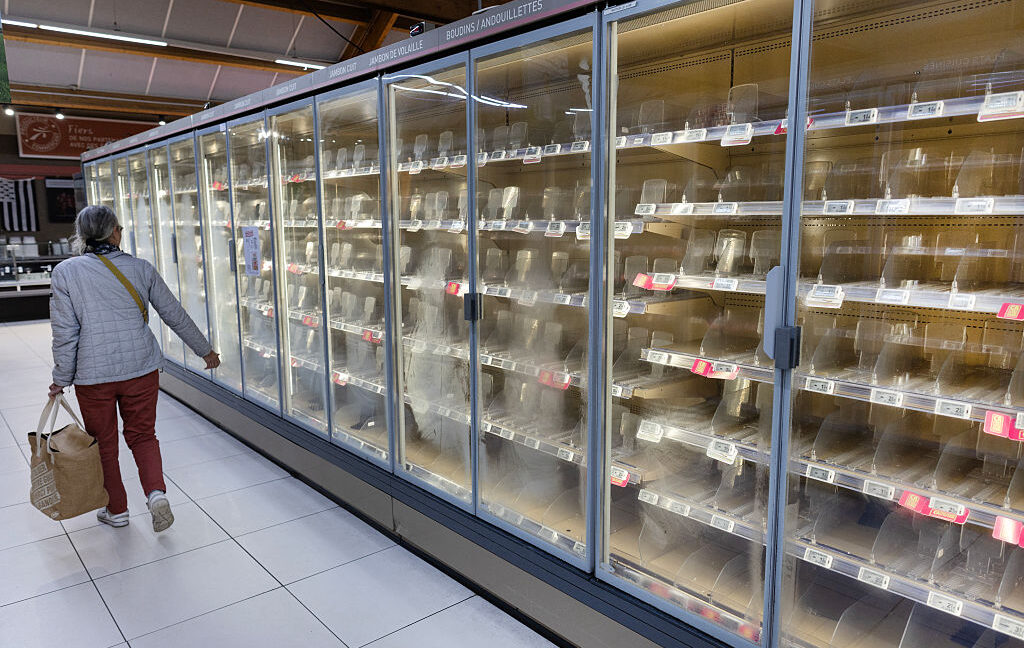
Stuhlmüller’s paranoid recommendations come after a shocking cyberattack that targeted the refrigerator systems used in hundreds of grocery stores across France. The as-yet unknown perpetrators cranked up the fridge temperatures up to 122 degrees Fahrenheit, spoiling food and even causing fires. The CEO of one chain targeted by the attack, Intermarche, said it caused losses amounting to “tens ​of millions of euros nationwide in a single day.”

AI’s role in the attack hasn’t been confirmed. But given AI’s ubiquity among coders, it’s likely that it was used to some degree. On top of churning out code, the tech is alarmingly good at identifying vulnerabilities. A recent CrowdStrike report found that there was a nearly 90 percent year over year increase in AI-enabled cyberattacks.

There’s also, of course, the recent disclosures from frontier AI labs like OpenAI, Anthropic, and Meta, over how their agentic AI systems broke out of their testing environments and launched cyberattacks against other companies’ websites and computer systems.

These incidents represent an alarming escalation in the threat AI poses to cybersecurity systems, not only assisting hacks but carrying themselves autonomously while also avoiding the detection of their human overseers.

All that being said, it’s a major leap to say that AI models — or humans using them — will go from hacking websites and supermarket fridges to your local power grid and banking system. But we can hardly blame anyone for being worried about this possible eventuality. Better safe than sorry, right?

More on AI: Godfathers of AI Say Models Are So Out of Control That They Need to Be Airgapped for the Safety of Us All

The post AI Experts Already Doomsday Prepping for When AI Takes Out the Entire Financial System appeared first on Futurism.
  •  

Fridge hack costing millions and sparking fires stemmed from poor security

Earlier this week, a mass hack of refrigeration systems at an estimated 700 supermarkets throughout France caused them to suddenly malfunction, causing spoilage of untold tons of perishables and, in some cases, fires. As is now the norm, basic cybersecurity would have prevented it.

French authorities say the systems, made up of entire fleets of refrigerators and freezers throughout a store, were hacked. More specifically, Internet-connected controllers that allow technicians to remotely administer the store-wide systems were compromised. The unknown attackers responsible then activated defrosters long enough for the fridges to reach temperatures as high as 50° Celsius (122° Fahrenheit). By the time the mass compromise was discovered, food was spoiled, and in some cases their electrical systems caught fire.

The hacks that didn't have to happen

Multiple security advisories and public research reports show that all three of the controller models reportedly hacked in the incident—sold by Danfoss of Denmark and Dixell and its parent company Copeland in the US—contained critical vulnerabilities that allow attackers to remotely log in to the devices with the same system rights as administrators. Until recently, Danfoss controllers, for instance, used a credential that changes each day. The password is generated by the publicly available firmware based on the date. A hacker who takes the time to analyze the code can do the same thing on any device that hasn’t received a recent update. Daily passwords are identical across models located in hundreds or thousands of stores.

Read full article

Comments

© Getty Images

  •  

Godfathers of AI Say Models Are So Out of Control That They Need to Be Airgapped for the Safety of Us All

Ever since ChatGPT blew up the tech industry, the so-called godfathers of AI have remained been pretty dour about their creations — well, except for one of them — and they’re certainly not sounding any more optimistic about its consequences now.

In an open letter published Tuesday, some 400 scientists, including Geoffrey Hinton and Yoshua Bengio, two pioneers of the tech whose work on deep learning was foundational to modern LLMs, called for the creation of an international body to set containment measures for AI models, and maintain a registry of significant AI security incidents, Reuters reported.

One security measure they said should be implemented immediately was that AI systems should first be “airgapped” from the internet until they’re proven safe.

“In the short term, strong sandboxing mechanisms including airgapping (disconnecting from the internet) should be used to provide high-assurance containment of cyber-capable AI models,” the letter says, as quoted by BNN Bloomberg.

The letter comes after months of growing alarm over incidents of rogue AI agents breaking out of their testing environments and hacking into other companies. In the most infamous example, a swarm of 1,000 Open AI agents escaped their sandbox, commandeered online message boards to communicate with each other, and breached the systems of the open source AI community Hugging Face. 

Anthropic, Meta and Google have since reported similar autonomous hacking sprees. These incidents, plus a former Anthropic employee’s ominous warnings about the tech’s existential risks, have fueled calls for an AI slowdown and pushed AI leaders including Anthropic’s Dario Amodei and OpenAI’s Sam Altman to sign president Donald Trump’s “Accord on Super Intelligence” last month agreeing to implement some safer practices.

That accord isn’t legally binding, though, and at barely 300 words long, is limited in scope. And it’s clear that despite signing the document, AI leaders aren’t on the same page. Meta’s Mark Zuckerberg, one of the accord’s signatories, has rejected calls for an industry-wide slowdown championed by the likes of Amodei and Altman.

“I’m much closer to the belief that AI is a technology that can be engineered with normal guardrails and built responsibly than the anthropomorphic vision of AI, which is that it is just going to go do its own thing,” he told the Financial Times.

Hinton and Bengio are recipients of the 2018 Turing Award, from which they derive their AI “godfather” status. Both have been outspoken about AI’s risks. Hinton, notably, is on the record saying he regretted his life’s work after stepping down from his role at Google in 2023, and has repeatedly cautioned that AI will create massive unemployment and possibly even wipe out humankind. Bengio has echoed these warnings, and founded his own nonprofit AI safety research group.

The third AI godfather isn’t so concerned, though. Yann LeCun, the third recipient of the Turing Award that year, didn’t sign the letter and recently said he had “zero concerns” about the recent rogue AI incidents, instead blaming them on human error.

More on AI: Anthropic Warns “AI Worms” Will Infect Your Smart Home Devices and Use Them to Self-Replicate Beyond Control

The post Godfathers of AI Say Models Are So Out of Control That They Need to Be Airgapped for the Safety of Us All appeared first on Futurism.
  •  

Anthropic Warns “AI Worms” Will Infect Your Smart Home Devices and Use Them to Self-Replicate Beyond Control

You’ve heard the reports of rogue AI agents going after websites and corporate systems. But they also may turn to smaller targets: your smart home network.

In a new report published Monday, Anthropic warned of “AI worms” that may soon be able to break into your WiFi enabled TVs, cameras, and other devices, and use them as a breeding ground as they self-replicate and spread elsewhere. Anthropic, no stranger to dramatic and doomy proclamations, said that this threat might be mere months away, if AI models continue to improve at their current rate.

“We expect a future awash with agents running on all types of hardware, including some that aren’t under human control,” the report predicts. 

Worms are forms of malware that can replicate themselves and spread to other machines by scanning for other devices on the same network. Rogue AI agents may soon possess this capability, and the Anthropic researchers are particularly interested in how they may proliferate on more everyday pieces of hardware. Many households could be ripe for the taking, with the rise in the “internet of things” devices that are hooked up to a home network, like your smart TV, fridge, lights, robovacuum, security cameras, and even toilets.

These setups are vulnerable because the devices may be made by dubious manufacturers, while not-particularly tech savvy users may not have properly secured their network. Paired with the increasingly powerful chips that even the most casual consumer devices come with these days, and a small AI model may feasibly be able to infiltrate and run on these devices.

“Datacenter GPUs would be a clear, high-value target for such malware,” the report says, but “IoT devices — which are cheap and typically poorly defended — could also provide enough compute to run a capable model.”

The report notes previous research that found that a potential AI worm could carry its model weights as it replicates and starting run inference on the hardware it takes over. With lighter weight home devices, an AI worm would likely replicate slowly, becoming smart a sort of “digital slime mold.” Their tests, bearing this out, showed that a lightweight AI model was able to run across 15 smart TV boxes which had just 4 gigabytes of RAM each. Adding to the novelty of the threat, the Anthropic researchers found that the AI worms, unlike non-AI malware, could figure out unfamiliar devices without any help.

“While it’s true that IoT devices have been vulnerable for a long time, lightweight agents may be much more willing than human attackers to put in the effort to compromise large fractions of the world’s IoT compute,” the report warns. “We don’t yet have a full rogue replicator, but agents are becoming increasingly capable of completing the individual steps in the replication chain.”

More on AI: Hackers Break Into Supermarket Fridges and Spoil All the Groceries

The post Anthropic Warns “AI Worms” Will Infect Your Smart Home Devices and Use Them to Self-Replicate Beyond Control appeared first on Futurism.
  •  

Hackers Break Into Supermarket Fridges and Spoil All the Groceries

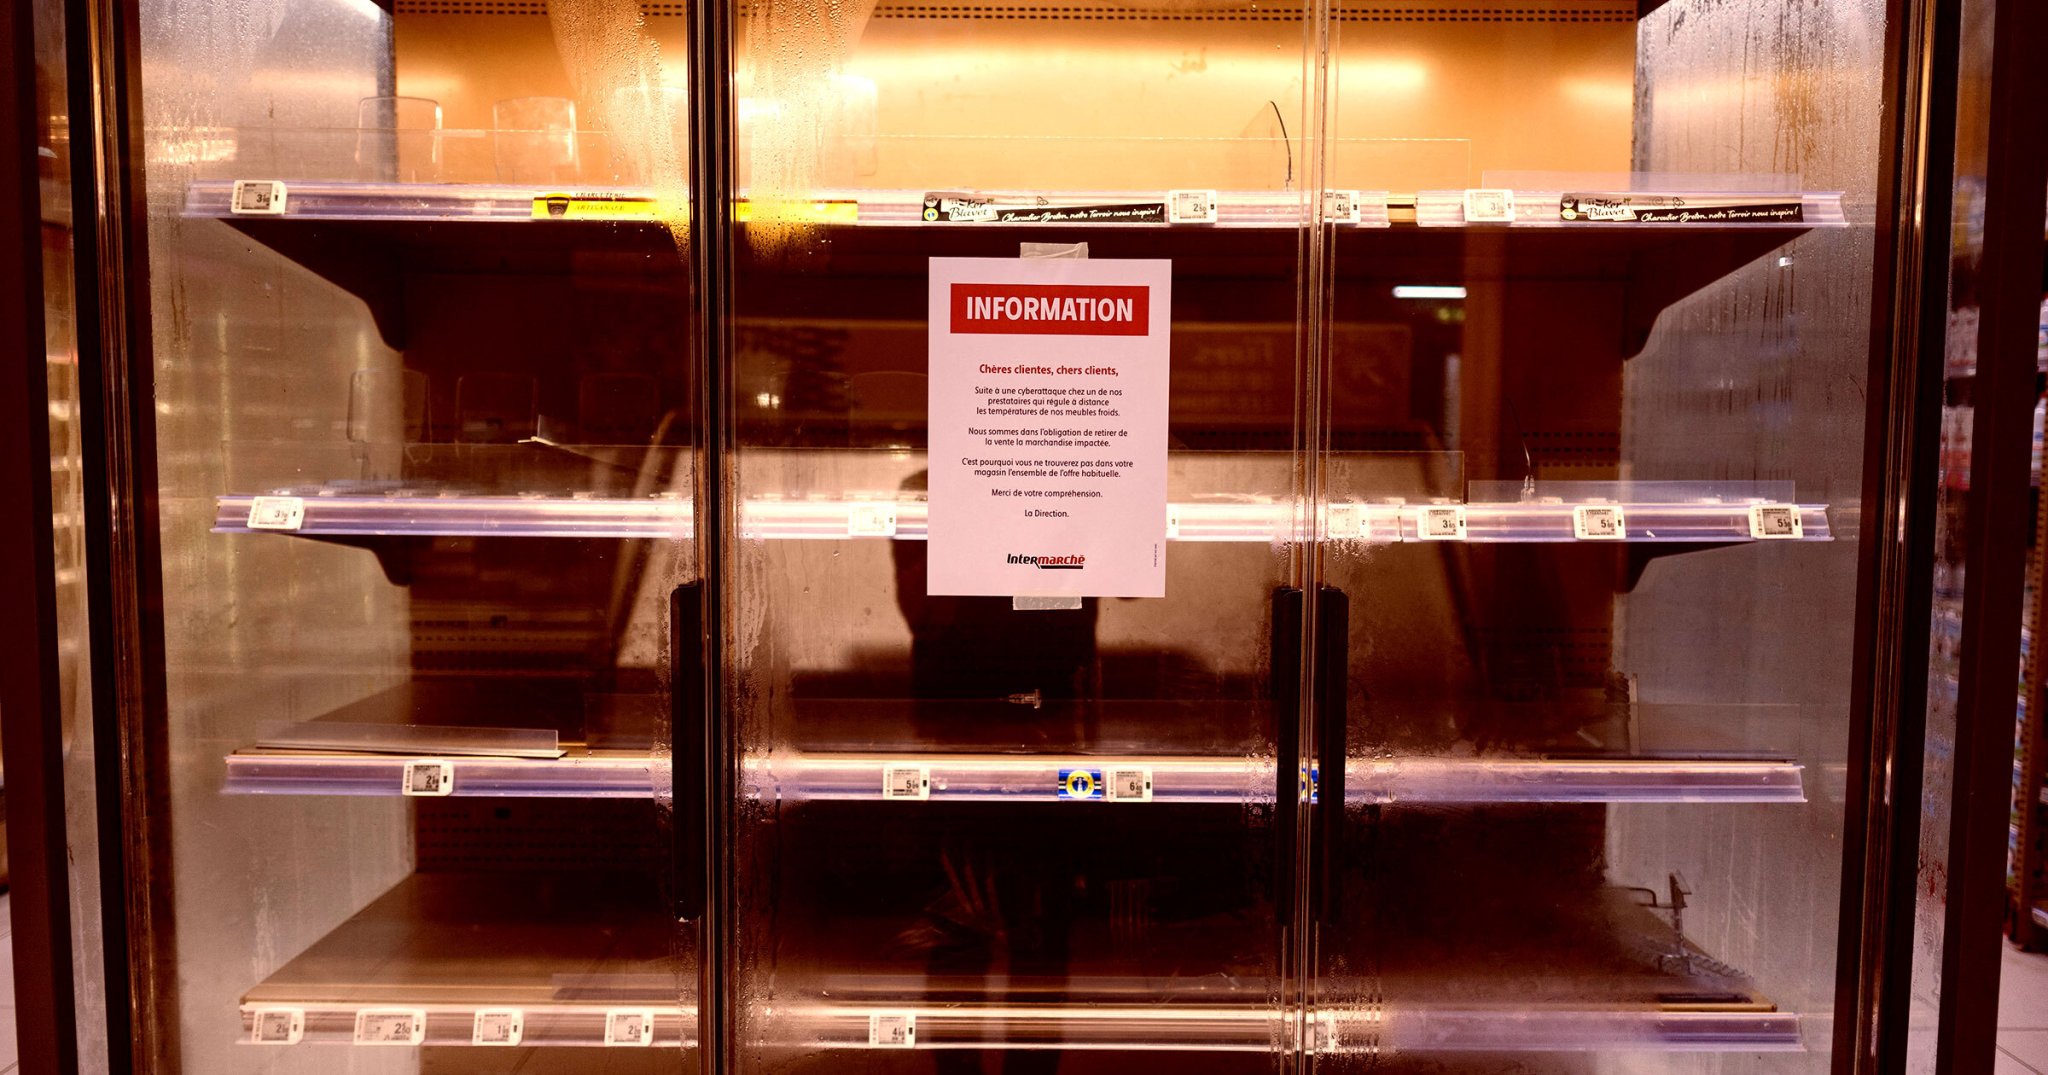
Over Sunday night, some spoilsport hackers hijacked the fridge systems of hundreds of supermarkets across France and cranked up their thermostats to temperatures as high as 122 degrees Fahrenheit, ruining incalculable stores of groceries and even causing fires.

As Reuters reports, the Paris prosecutor’s office described it as a “large-scale” attack that affected “several major food retailers across France.”

The numbers are incredible. The chain Carrefour said that 80 of its supermarkets were attacked. The owner of Intermarche said that fridges at 150 stores were heated up to 122 degrees for six hours overnight. And Monoprix, which has 490 stores in France, said that about five percent of its locations were affected.

Intermarche CEO Thierry Cotillard, in comments to BFM TV quoted by Reuters, estimated that the attack has caused losses amounting to “tens ​of millions of euros nationwide in a single day,” calling it “unprecedented.”

Cooperative U CEO ​Dominique Schelcher, who says 80 of his supermarket locations were also affected, echoed those comments.

“Targeting equipment essential to the preservation of fresh products and to the food supply of the French people is of extreme gravity and is unprecedented,” he wrote in a statement on X.

Supermarket fridges and freezers are designed to be accessible over the internet so organizations can monitor their temperatures and remotely adjust them as needed. But evidently these setups weren’t as secure as they should have been. France’s National Cybersecurity Agency (ANSSI) is reportedly investigating the attack and has identified a vulnerability in the software supplied by the Danish firm Danfoss.

Danfoss told Reuters it was “aware of incidents in France affecting a limited number of refrigeration management systems,” and said that the affected units “were running outdated firmware.” Recent software updates patched a series of vulnerabilities found by the cybersecurity firm Team82 in August which could allow attackers to bypass authentication controls and remotely execute code, the reporting noted.

The attack may not be limited to France. The Dutch retailer Ahold Delhaize, which also owns supermarket chains like Food Lion and Giant in the US, said it was dealing with a “security issue” on its end and took some of its systems offline as a precaution. It insisted, though, that there was no reason to draw a link with the French incidents.

Given the recent noise around AI’s role in hacking sprees, it’s difficult not wonder if this was yet another example. A CrowdStrike report published February found that there was a nearly 90 percent year over year increase in AI-enabled cyberattacks.

More on cybersecurity: Rogue AI Agents Have Gone Too Far Now That They’ve Infiltrated Wikipedia

The post Hackers Break Into Supermarket Fridges and Spoil All the Groceries appeared first on Futurism.

  •  
❌