❌

Reading view

Samsung and SK Hynix are upgrading Chinese factories to produce advanced RAM chips as AI data center competition ramps up

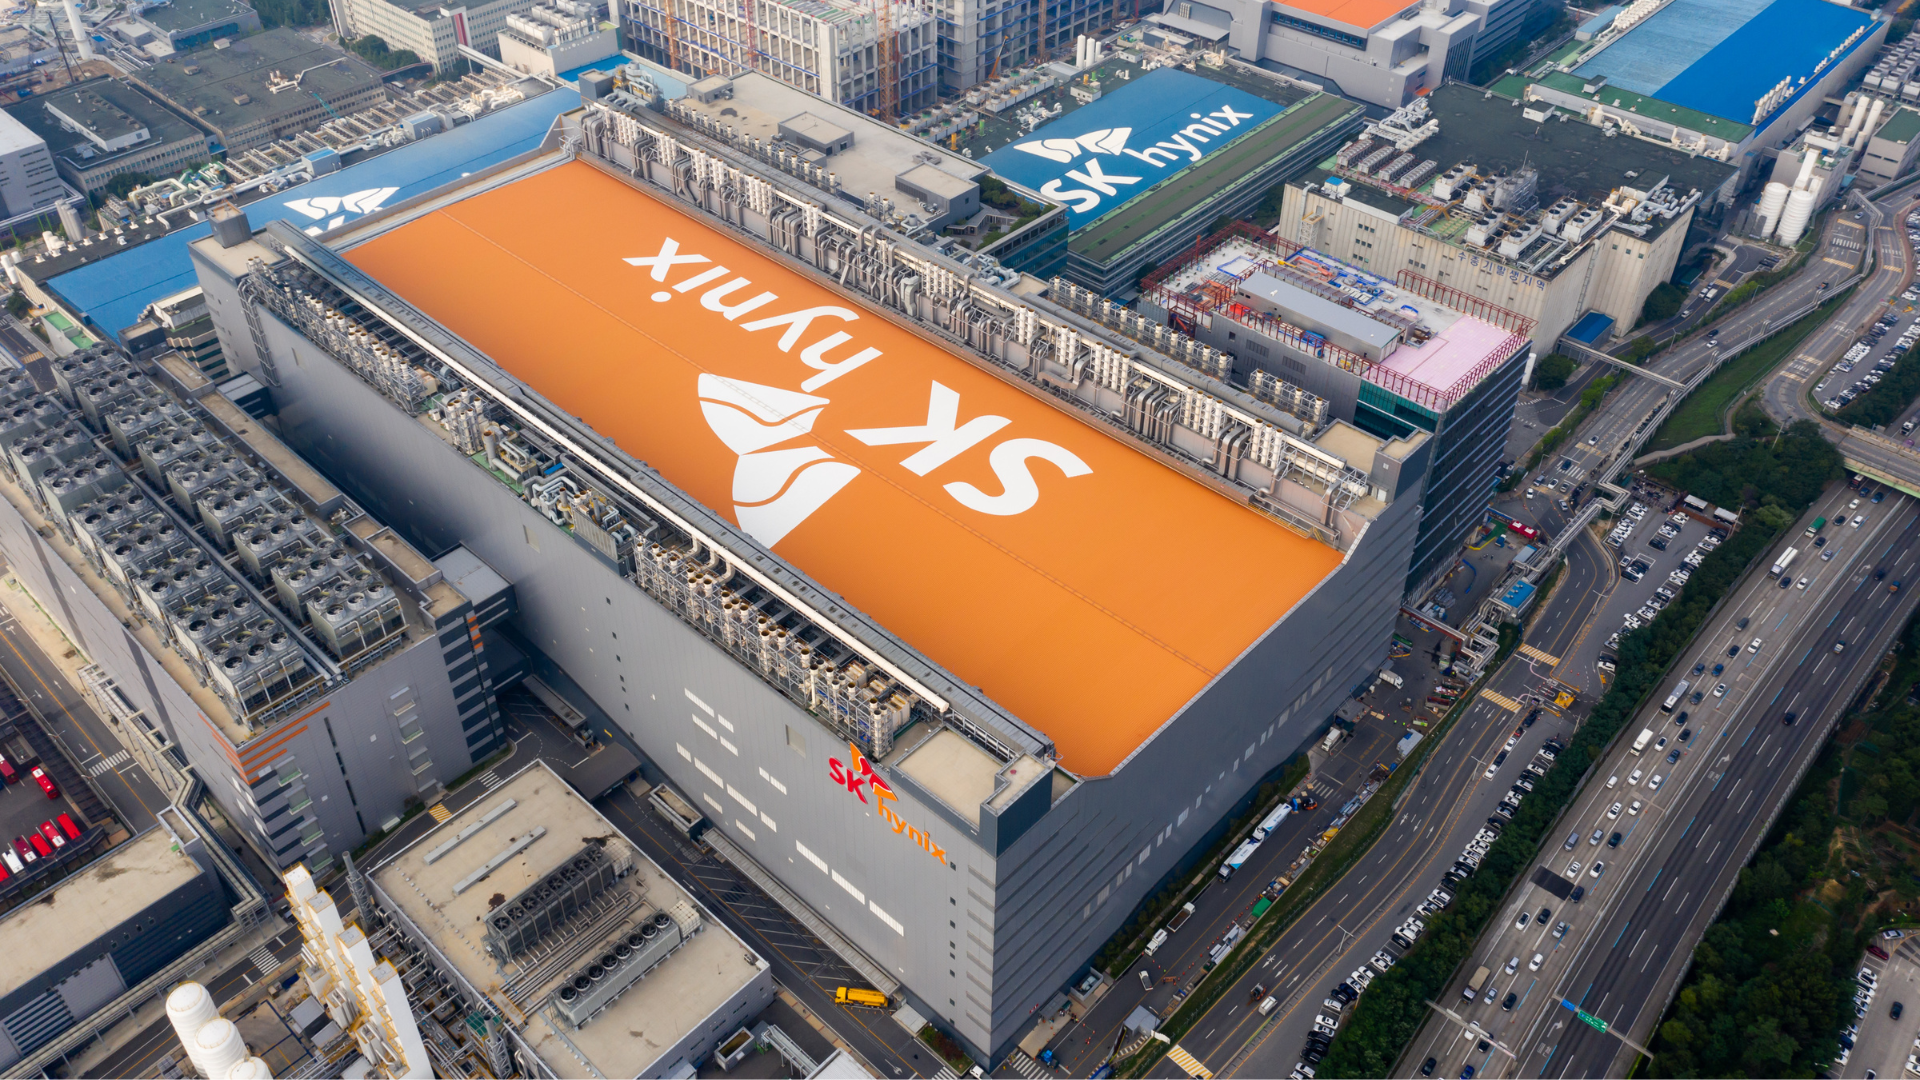
The two biggest NAND flash memory manufacturers on the planet, Samsung Electronics and SK Hynix, are reportedly working to upgrade their Chinese factories to produce more advanced chips for use in AI data centers, Reuters reports. The move comes as the two companies continue to fight off competition from the fast-growing Chinese memory makers like CXMT. Fierce competition in the lucrative AI RAM market has already seen manufacturers slash consumer-focused production to allow them to increase production capacity for the more advanced β€” and money-spinning β€” components.

Citing four people familiar with the companies' plans, the report claims that Samsung Electronics aims to switch its Xian plant to the production of 286-layer flash chips by the end of the year. SK Hynix has its sights set a little lower, targeting chips with 240 or more layers at its Dalian facility. That factory was taken over back in 2021, but a timescale for the new upgrades isn't clear.

However, while Samsung Electronics and SK Hynix are well placed to deal with the growing threat from Chinese chipmakers, both are faced with additional complications in the form of U.S. regulations. Export controls on chipmaking equipment were applied in 2022, with the aim of slowing China's technological progress. Both companies, based in South Korea, must now get licenses in order to install U.S.-built hardware in Chinese factories. The report points to this as a reason for the recent growth of Chinese firms like Yangtze Memory Technologies Co. (YMTC). The company told investors at a recent IPO preparation meeting that it aims to become the world's largest NAND flash producer by the end of 2027.

While both Samsung Electronics and SK Hynix say that they are working in consultation with the U.S. authorities, there's little doubt that this extra step has hampered the companies' ability to upgrade their factories to better meet the new AI memory demand.

It's impossible to overstate just how key Samsung and SK Hynix are to NAND supply. Samsung's Xian factory produces around 40% of the company's global output. It currently produces chips that have around 200 layers, but Samsung's plans aim to boost that to 286 layers for V9 NAND chips. For its part, SK Hynix's Dalian plant currently produces chips with 192 layers, with the company's aim for 240-layer chips reportedly confirmed by three people familiar with the plans.

Meanwhile, CXMT, China's premier chipmaker, is looking to move beyond DRAM production. A report from September 2026 noted that it was eyeing production of 3D NAND memory for use in solid-state storage (SSD) products. The country's largest DRAM producer, CXMT, posted $22.41 billion in revenue and $11.57 billion in net profit in the first half of 2026 after years of losing money. But despite this purple patch, the company is still much smaller than the likes of Samsung, SK Hynix, and Micron.
Google Preferred Source

  •  

Chinese crime ring steals more than $5 million in gift cards from Staples customer service

Millions of dollars worth of gift cards were stolen and then used to buy high-value tech gear at retailers like Target, Sephora, and Lowe's after a Chinese crime ring gained access to an internal Staples system and then used it to issue more than 15,000 cards to itself. While the hack hasn't been made public to date, a 404 Media report notes that it actually took place back in 2023.

The outlet reviewed court records that show that Homeland Security Investigations (HSI) was told about the hack in October of that year. The hack came to light after it led to a search warrant that was unsealed last week. And while the document doesn't specifically name Staples as the victim of the hack, 404 Media has confirmed that it was the company affected based on other information. Such information includes the fact that the victim company is headquartered in Massachusetts, that it uses Blackhawk Networks to fulfill gift card orders, and that the company uses an internal customer support system called Nexus. The report notes that a reference to Nexus can be found on a former Staples executive's LinkedIn profile.

While Staples was under the impression that Nexus could not be accessed from beyond its own network, hackers found that not to be the case. They then "performed multiple heap dump requests," a process that captures all of the data held in an app's memory. That information gave the hackers the tools they needed to hijack logged-in sessions of Staples customer service employees. From there, they were able to issue gift cards at will.

Once the gift cards had been issued, the crime group sent runners to physical retail stores to spend them before they were identified and canceled. Target found that 35 gift cards were used at a New Hampshire store, with high-value products from Apple, Bose, and Beats all bought. All 35 cards were used within a period of just a single hour, although not all of them were obtained via this hack.

In total, Target told investigators that 3,850 gift cards worth over $140,000 were used across 85 different stores in just two days. Sephora was hit for $58,600 worth of sales, while Lowe's saw $226,000 spent across online and in-store purchases. In total, 4,630 stolen gift cards were used with a value of around $425,000.

This hack was just the tip of the iceberg, too. Last April, a Department of Justice announcement confirmed that three Chinese nationals had been sentenced for their part in a gift card fraud conspiracy. Including the Staples hack, the crime group stole more than $100 million worth of gift cards.

Chinese organized crime groups often pop up on the radar of U.S.-based law enforcement. Earlier this year, a Chinese phishing service that was used to generate scam websites using AI was dismantled. The service was linked to almost $2 billion in losses.

Google Preferred Source

  •  

A Chinese hacker used AI agents to break into more than 100 company websites

A Chinese-speaking hacker has been observed using artificial intelligence (AI) agents to probe and then gain unauthorized access to more than 100 websites belonging to some extremely well-known companies. From Deere, the farming equipment manufacturer, to SharkNinja, the company behind beloved kitchen appliances, the agents were able to leverage exposed instances of Carin, an open-source AI-powered problem-solving platform that has proven popular among hackers, a Reuters report explains.

This is just the latest example of hackers turning to AI agents in an attempt to level up their attacks on unsuspecting companies and services. Snorre Fagerland, principal threat researcher at the cybersecurity company NorForge, spotted the hacker's antics when observing Carin instances that had been inadvertently exposed.

Fagerland was able to watch multiple hackers go about their business, but the Chinese-speaking hacker was the most prolific, the report says. They targeted businesses based in the United States, Canada, Australia, and Japanese e-commerce sites. Notably, the hacker didn't get into detail when commanding their legion of AI agents. Fewer than 100 Chinese characters were used, yet the agents had attempted ot break into more than 1,200 different websites as of the week ending October 18, 2026.

These agents weren't simply throwing everything at a wall and hoping it stuck, either. Security researcher Fagerland was "impressed" by some of the tactics that had been used. In one case, the AI agents scoured digital records to find infrastructure associated with their target, located a public-facing control panel, identified a weakness, and then leveraged it to force the execution of malicious commands, the Reuters report detailed. "It's ⁠not straightforward to come up with solutions like that," Fagerland told Reuters. "It's not script kiddie stuff."

Vitally, the approach of using AI agents in this way means that they can be given instructions and then left to their own devices. With no supervision required, those commanding the agents are free to turn their attention elsewhere. While SharkNinja told Reuters that the attack only impacted a site used for product support information, the rest of the AI-aided hackers had more luck. One of the hackers monitored by Gargerland stole credit card data, while another tried to steal from a cryptocurrency exchange β€” although it isn't clear whether they were successful.

Google Preferred Source

  •  

AWS tells clients to quit Middle East data centers six months after Iranian drone strikes β€” Amazon offers no recovery timeline as UAE mulls underground data centers [Updated]

More than six months after Amazon Web Services (AWS) data centers in Abu Dhabi and Bahrain were attacked by drones, the company has now had to tell customers to move their data to facilities in other regions. The Wall Street Journal reports that AWS has admitted that it's time for customers to jump ship to data centers located elsewhere in the world. In its AWS dashboard update, AWS confirmed "most customers have been able to re-establish their operations in other Regions by restoring backups or copying data that remained accessible. AWS Support remains available to help customers who need assistance moving their applications to alternate Regions."

The move comes as AWS continues repairs on the damaged data centers, but it stopped short of offering a timeline as to when customers can expect either location to be back online. AWS says that it remains committed to supporting its customers in Bahrain, but only said it would provide a further update early next year. It did not offer any specific recovery time frame for the restoration of services. Regarding the UAE, AWS says that it is working to replace affected infrastructure, but again only said it would provide an update on the restoration of services in the coming months.

Both affected data centers became targets for the Islamic Republic of Iran after the United States and Israel launched strikes on that country in February of this year. Months later, the Bahraini data center was struck by cruise missiles, and Iranian state media claimed it had been "destroyed."

The move is bad news for the United Arab Emirates. The U.A.E. has spent years trying to become a world leader in data processing, a pitch that led it to lobby U.S. officials to allow it to buy AI chips for its data centers.

Having made plenty of noise about OpenAI's decision to take a spot in a 5-gigawatt data center complex in May 2025, U.A.E. officials have since seen those plans stall. The WSJ points out that no lease has been signed well over a year later. OpenAI was expected to take 20% of the data center's total capacity, the kind of loss that is sure to sting officials if plans don't get back on track.

For its part, the U.A.E. is clearly well aware of the threat that the ongoing regional instability poses to its ambitions, and it's looking for ways to address the fears of potential partners. Officials have already hinted at the potential for underground data centers. While the move would make an already costly endeavor even more expensive, it could help defend new data centers from drone attacks. Building drone defense systems near data centers is another option.

Drone attacks can be catastrophic for any building, and data centers are no different. The data centers operated by AWS suffered fires and damaged infrastructure as a result of the strikes. In their efforts to fight the fires caused by drone strikes, emergency workers used water, causing further damage.

The Abu Dhabi and Bahrain data centers are relied upon by a variety of businesses in the banking and financial sectors. Those businesses cannot tolerate downtime, especially of the protracted variety. There's little sign of data centers slipping from the crosshairs of drone operators any time soon, either, and AWS is far from unique in finding its data centers under attack.

Iran's Islamic Revolutionary Guard Corps (IRGC) claimed in April that it had hit a data center linked to Oracle in Dubai. That unit further threatened American tech companies, including Microsoft, Oracle, Alphabet, and Nvidia, this spring. It accused the companies of contributing to attacks on Iran. With that in mind, and with tensions in the Middle East looking unlikely to ease any time soon, it's perhaps unsurprising that AWS has asked customers to move data to safer data centers around the world.

Google Preferred Source

  •  

AI enthusiast builds GPT-6 Astra-powered bot to take on Balatro's Gold Stake Black Deck β€” bot leverages Python for numerical tools, beats hardest difficulty repeatedly

A Reddit user has shared details of a new bot that has beaten the devilishly difficult Gold Stake Black Deck in Balatro, a poker-like video game. The Redditor, who works in the AI industry, says that they have been testing the bot and "obtaining some crazy results" β€” and they've even shared a YouTube video highlighting how they went about creating the card shark of a bot.

In a post in the /balatro subreddit, user Atol8 (real name Jacopo Attolini) initially claimed the bot was the first of its kind to reliably beat Balatro. They subsequently admitted that "reliably might be a strong word," adding that the bot has "repeatedly beaten Balatro."

My Balatro Bot just won at Gold Stake Black Deck
Β fromΒ r/balatro

Beating Balatro in this instance meant beating the Gold Stake Black Deck, a combination that is widely considered to be the most difficult in the game. On its own, the Black Deck includes +1 Joker slot, but reduces the player's available hands by one per round. The Gold Stake effect introduces cumulative difficulty modifiers from all prior stakes, plus reduced hand sizes and stricter economic penalties.

Combining these two together makes for a brutal economy and more than a little luck, with players relying on strong early-game RNG.

In a post in the /balatro subreddit, user Atol8 (real name Jacopo Attolini) initially claimed the bot was the first of its kind to reliably beat Balatro. They subsequently admitted that "reliably might be a strong word," adding that the bot has "repeatedly beaten Balatro."

Beating Balatro in this instance meant beating the Gold Stake Black Deck, a combination that is widely considered to be the most difficult in the game. On its own, the Black Deck includes a +1 Joker slot, but reduces the player's available hands by one per round. The Gold Stake effect introduces cumulative difficulty modifiers from all prior stakes, plus reduced hand sizes and stricter economic penalties.

Combining these two together makes for a brutal economy and more than a little luck, with players relying on strong early-game RNG.

The bot itself is based on OpenAI's Astra models, which were released earlier this month. GPT-6 Astra has already grabbed headlines, having completed Valve's iconic Portal in 24 hours.

In a GitHub post detailing the ins and outs of the bot, Attolini says that GPT-6 Astra takes care of making strategic decisions based on the deck it has built. But the bot also relies on good old Python for its numerical tools. The legality of each move is assessed by BalatroBot, a separate tool that exposes Balatro game states and controls for external programs to interact with.

As impressive as this is, don't be fooled into thinking this bot played the perfect game. Reddit commenters have been quick to point out that it made some "interesting blunders" throughout its playthrough. Despite that, GPT-Astra is OpenAI's latest flagship model, with the company claiming it offers β€œa new generation of intelligence,” and β€œis state-of-the-art on computer use, browsing, software engineering, cybersecurity, science, and professional work.”

Not all bots are great at playing games, though. Just last year, OpenAI's ChatGPT "got absolutely wrecked on the beginner level” while playing Atari Chess. Elsewhere, Google's Gemini didn't even get as far as starting its own chess battle with the Atari 2600 β€” it ditched the game after deciding that it would "struggle immensely" against the iconic home console. It seems that, sometimes at least, even modern tech can't compete with a 1979 Atari 2600 game.

Google Preferred Source

  •  

Nvidia, Palantir, and others restrict advanced AI model usage over privacy concerns, report claims β€” 'paranoia' rising over customer intellectual property

Anthropic and OpenAI are both facing uncomfortable questions from some large AI customers over concerns about how proprietary data may be used to train AI models. Some companies are so worried that they have begun demanding assurances about how their data is handled or going so far as to place limitations on which models their employees can use, and for which tasks, The Information reports. They fear that models may be trained on their intellectual property and information.

The issue can be traced back to a June change by Anthropic. Following the change to its flagship Fable model's policies, Anthropic can now retain customer data. The company argues that it only does so to ensure that Fable isn't being misused. But some companies have raised concerns that it means sensitive business data will be caught up in the sweep.

While both OpenAI and Anthropic point out that they don't train their models on the information given to them by companies with specific enterprise contracts by default, that doesn't tell the full story. Both companies do collect metadata from the same corporate customers, and while information on exactly what that metadata contains is hard to come by, OpenAI notes that it's only used β€œto better understand how our services are used." Anthropic also argues that any data it collects about how customers use its products is aggregated and anonymized. And that metadata isn't used to train models.

Regardless, there are still concerns over a perceived lack of clarity about what is collected. Telecoms outfit C Spire has agreements with both OpenAI and Anthropic that prevent either from using its data to train models, the report says.

However, the contracts do allow both OpenAI and Anthropic to collect C Spire technical usage data. C Spire believes that includes information about what applications AI models are connected to as well as usage data. It also worries that the AI companies may collect information about what their models get up to between generating responses.

For its part, OpenAI says that it does not use this "chain-of-thought" data to train its models. But C Spire still believes it needs a better understanding of what data is being collected, the report adds. It argues that neither AI company is being clear in its explanations.

Taking the private approach

One solution to any privacy concerns could be to use air-gapped servers, something aerospace company Northrop Grumman has already chosen to do. The Information reports that the company runs open-source AI models on its own air-gapped servers rather than trusting the likes of OpenAI and Anthropic.

Alternatively, Microsoft is already trying to take advantage of any data privacy concerns by tempting OpenAI and Anthropic customers to its own secure AI platforms. Microsoft's isolated cloud environments run AI models on private servers that don't send any data to external AI companies. But this approach is costly, and the report notes that at least one customer is still considering Microsoft's alternative approach.

Pharmaceutical company Novo Nordisk has taken a slightly different approach. While it continues to use Anthropic's Claude for some tasks, it has a ban on allowing any proprietary data to be used by the model.

It's clear that a lack of trust has the potential to cost AI companies real money, and in one instance, it already has. The same report notes that a large U.S. utility company has already canceled its plans to test Anthropic's Fable. The utility company wanted to know if Fable could run its core power infrastructure but ultimately pulled the plug over Anthropic's refusal to agree to a nonrevocable zero data retention (ZDR) policy.

Nvidia has also decided to use Fable for tasks that don't require it to gain access to sensitive data. The company points to the same lack of ZDR guarentees as the reason. Instead, Nvidia uses its own in-house AI solution for tasks that it deems too sensitive for Anthropic's model. Nvidia CEO Jensen Huang has famously remarked that its employees should use AI tokens worth half their annual salary every year.

Toms Hardware reached out to Nvidia for comment but did not receive one by publication.

  •  
❌